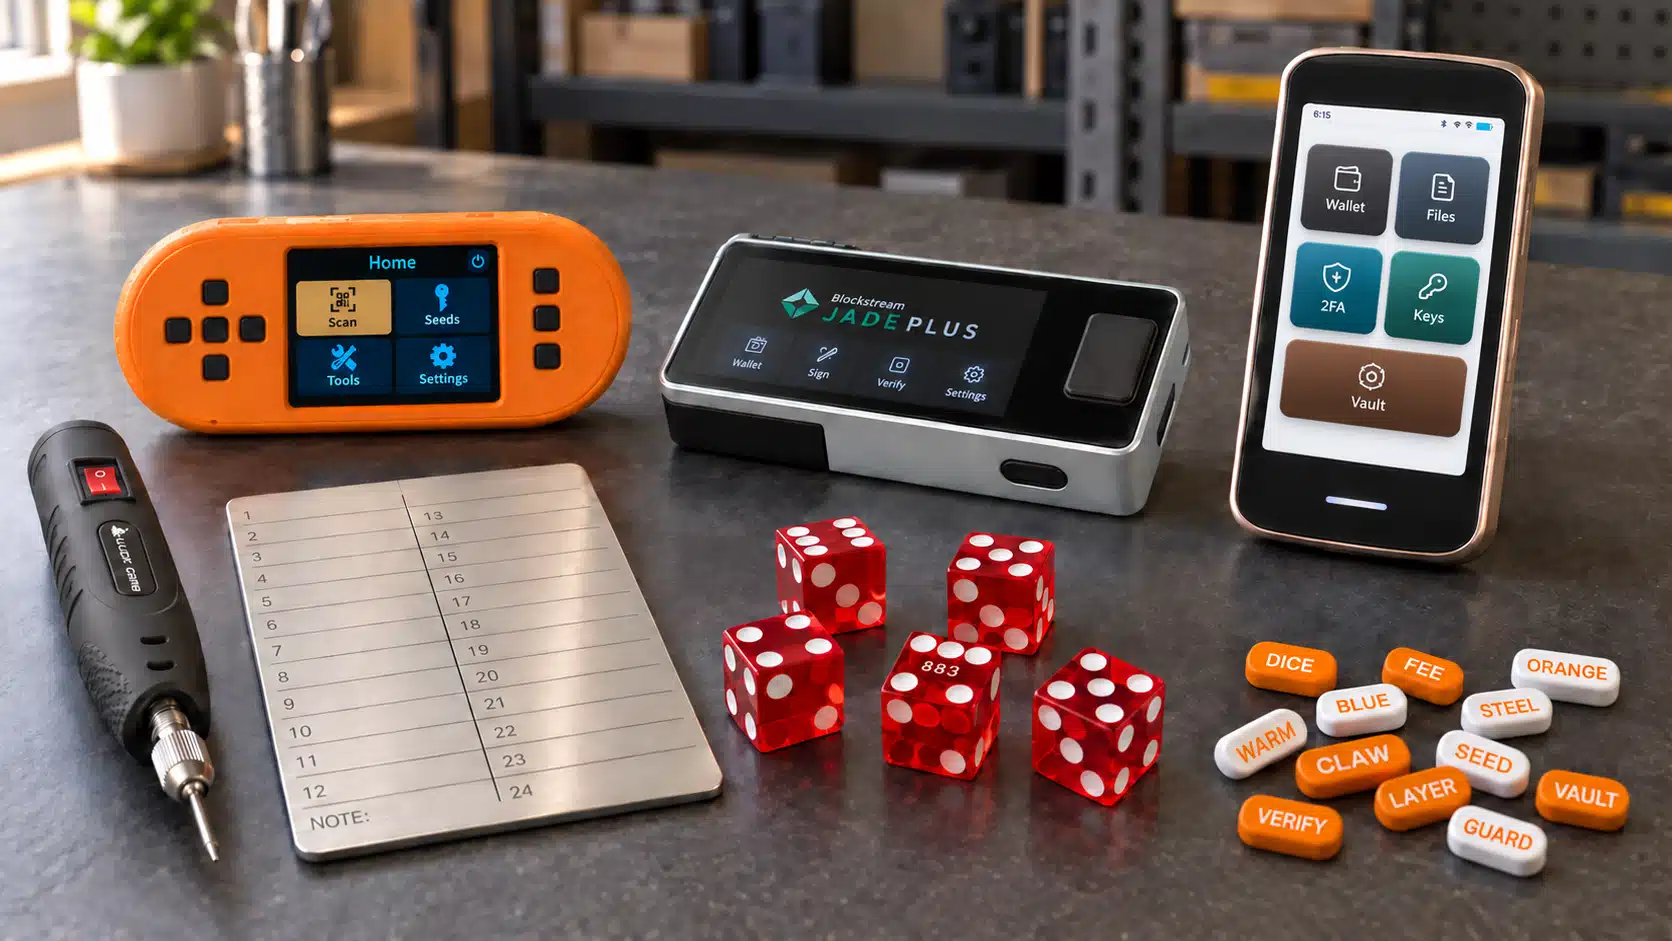
To protect your bitcoin in 2026, do five things: hold your own keys on a hardware wallet, generate the seed with randomness you supplied yourself, back it up in steel in more than one place, verify every address on the device screen, and keep quiet about what you own. Those five steps cover every major way people lost bitcoin this year. That includes the $282 million support-impersonation theft in January, the Coldcard entropy sweep in July, and the record pace of home-invasion “wrench attacks.” This guide is for anyone holding bitcoin, whether it is still on an exchange or already on a wallet you set up years ago.
Key takeaways
- In 2026 the attacks that actually drain individuals are social engineering, weak seed generation, and physical coercion, not broken cryptography. Bitcoin’s math has never been the problem.
- A hardware wallet only protects you if you never type the seed anywhere, never share it with “support,” and confirm every receive address on the device screen.
- The Coldcard incident (July 30, 2026, roughly 1,367 BTC swept in the first three days) proved that the randomness behind your seed matters as much as where you store it. Add your own dice or Entropia entropy.
- Chainalysis counted 46 violent “wrench attacks” and more than $30 million stolen in the first half of 2026. Privacy is now a security control, not a preference.
- A steel backup, a tested restore, and a written inheritance plan protect you from the most common loss of all: your own mistakes.
Terms you’ll see
- Seed phrase: the 12 or 24 words that can rebuild your entire wallet. Whoever has them has your bitcoin.
- Hardware wallet / signing device: a small offline gadget that keeps the seed and approves transactions without exposing it to your computer.
- Entropy: the randomness used to create a seed. Weak randomness means a guessable seed.
- Air-gapped: the signing device and your computer never share a data connection; they swap information by QR code or memory card.
- Passphrase: an optional extra word or sentence that unlocks a second, hidden wallet from the same seed.
- Multisig: a wallet that needs more than one key (for example 2 of 3) to spend anything.
- Node: your own copy of the Bitcoin blockchain, so you can check balances without asking a company’s server.
What are the biggest threats to your bitcoin in 2026?
The biggest threats to your bitcoin in 2026 are people-and-process failures, not broken math. The five that matter: scams that talk you out of your seed, wallets that generated weak seeds, poisoned addresses in your transaction history, physical coercion, and plain old lost backups.
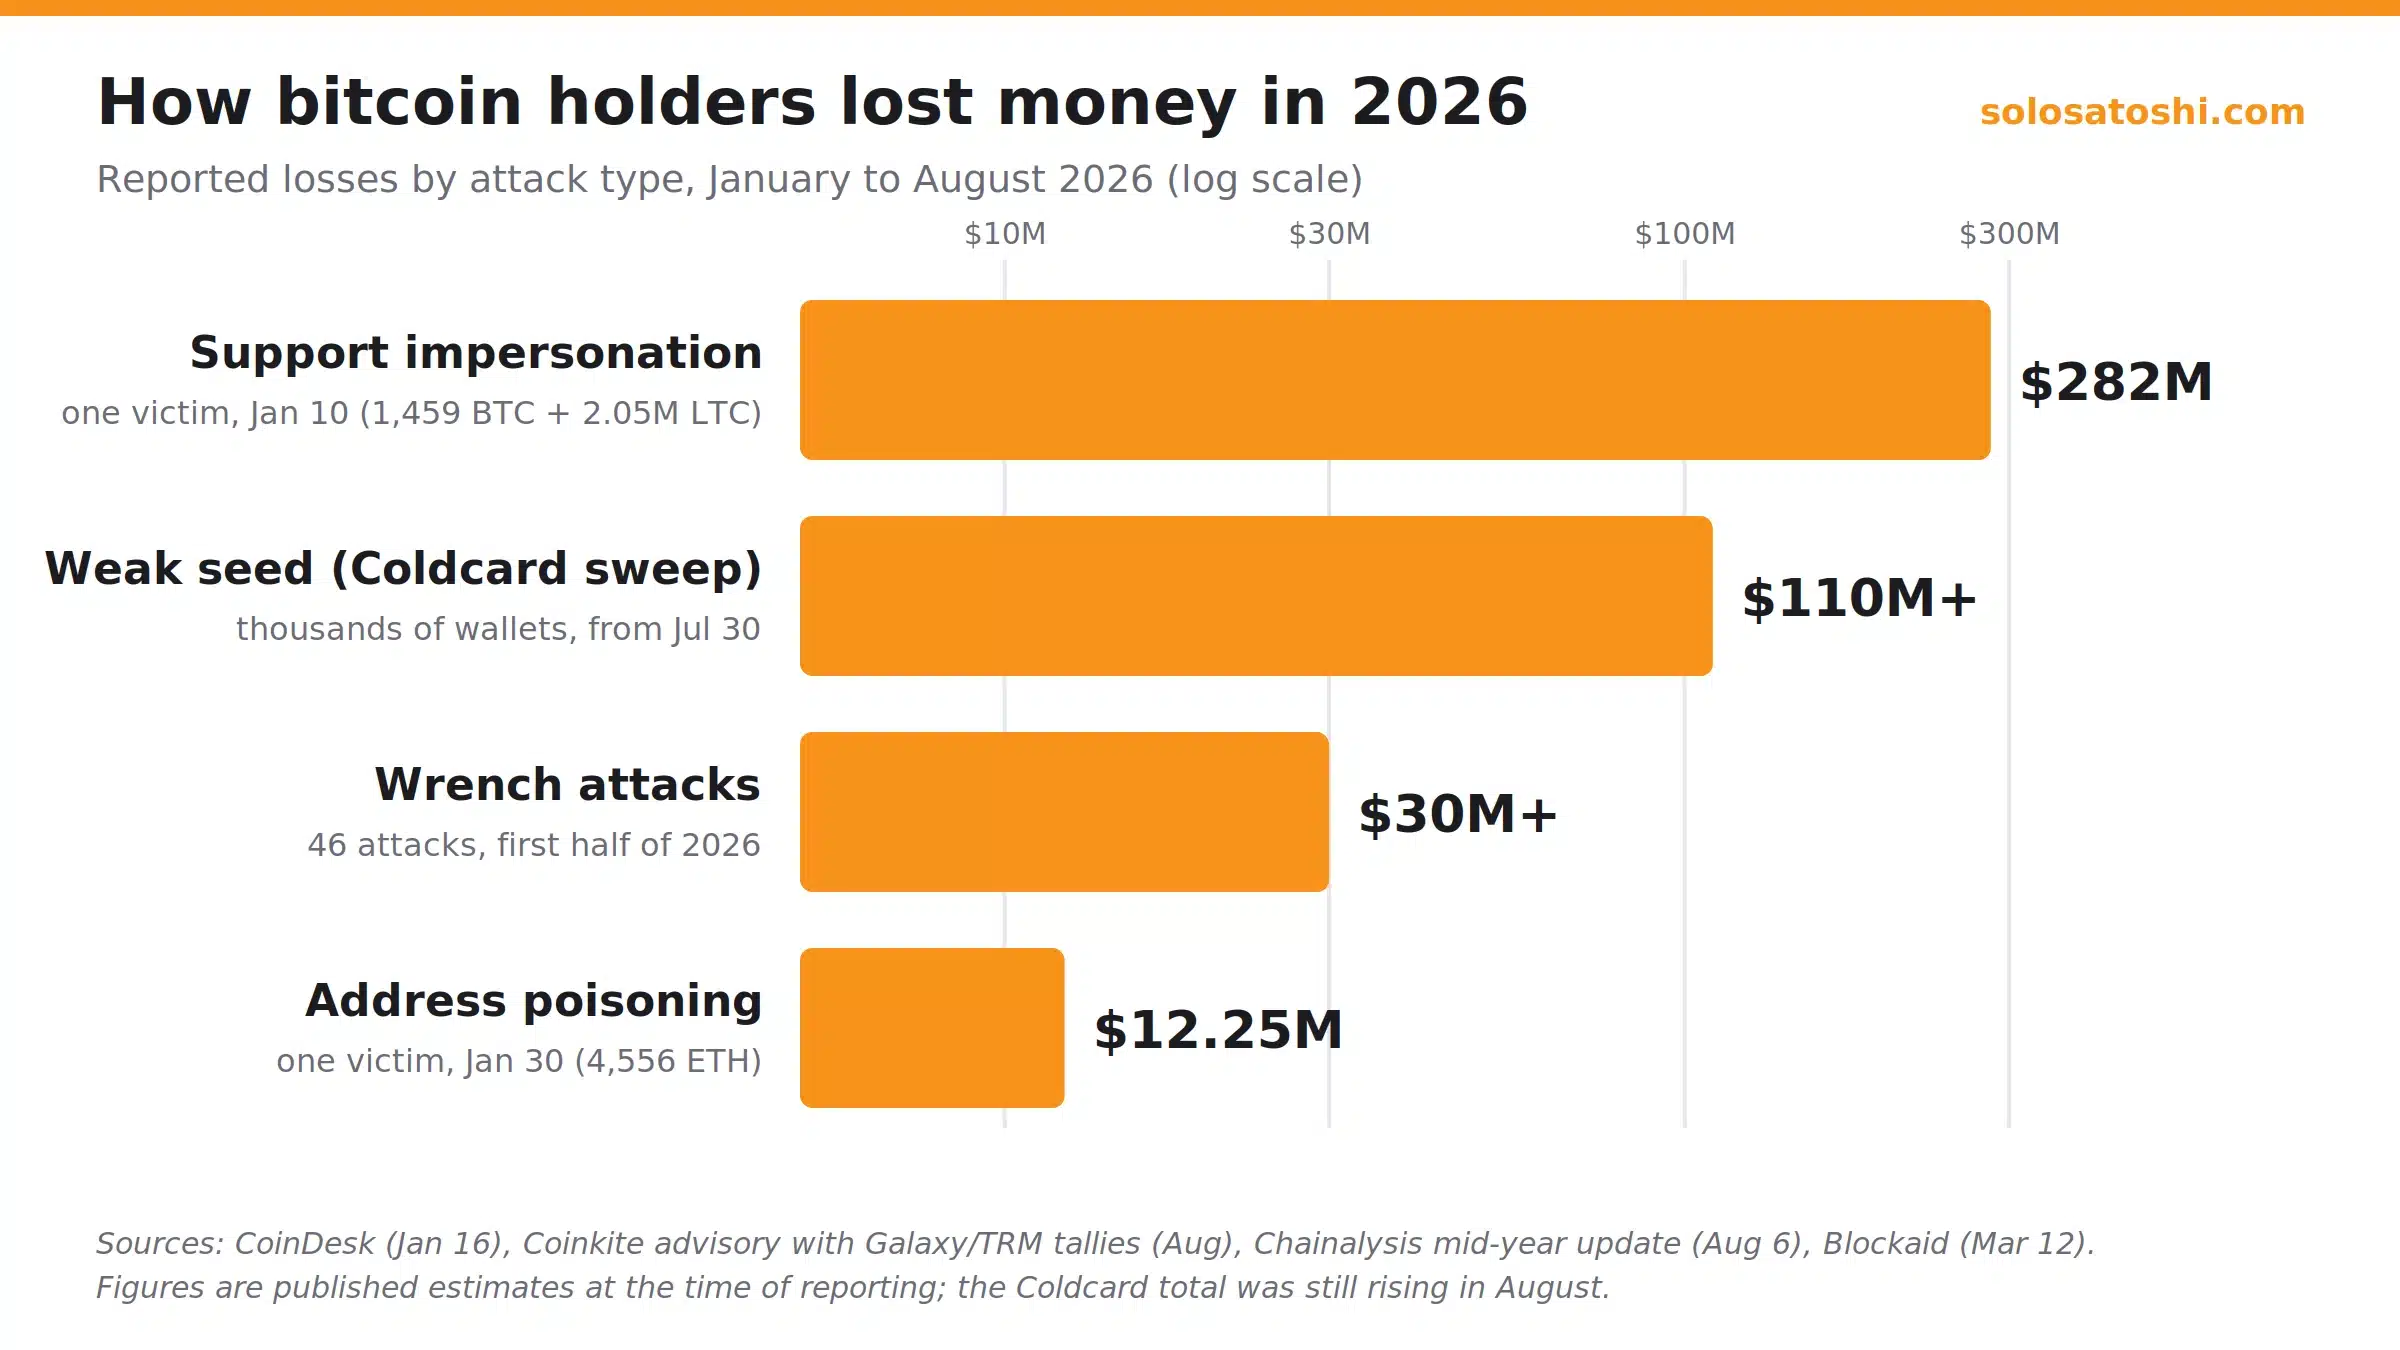
None of this year’s headline losses involved breaking Bitcoin’s cryptography. Security firm Hacken counted about $306 million lost to phishing and social engineering in the first quarter of 2026 alone, nearly two-thirds of all losses it tracked. Most of that came from a single January incident in which one holder was talked into handing over a hardware wallet backup. The table below lists the threats we think matter most for an individual holder, with a real 2026 example of each and the defense that stops it.
| Threat | 2026 loss | One-line defense |
|---|---|---|
| Support impersonation | $282M, one victim (Jan 10) | Never share the seed |
| Weak seed generation | ~1,367 BTC, Coldcard (Jul 30) | Add your own entropy |
| Address poisoning | $12.25M, one victim (Jan 31) | Verify on the device screen |
| Wrench attacks | $30M+, 46 attacks (H1) | Privacy and off-site keys |
| Malware | Ongoing | Air-gapped signing |
| Lost backup | Most common, unreported | Steel, two places, tested |
Support impersonation and social engineering
What it looks like: a call, email, or DM from “wallet support” asking you to verify, restore, or upload your recovery phrase. On January 10, one victim lost 1,459 BTC and 2.05 million LTC, over $282 million, after an attacker posing as hardware-wallet support obtained their backup. No vendor ever needs your seed. Never type it into anything with a screen and a network connection.
Weak seed generation
What it looks like: a wallet’s random number generator silently produces a guessable seed. It looks and works normally until it is swept. On July 30, 2026, Coldcard seeds created on affected firmware since 2021 were brute-forced, and about 1,367 BTC were gone in the first three days. Mix your own dice or Entropia entropy into every new seed, and prefer devices that let you.
Address poisoning
What it looks like: dust sent from a lookalike address so that you copy the wrong one from your history next time. On January 30, a single copy-paste mistake cost one user 4,556 ETH, about $12 million, after the attacker had dusted their wallet for two months; the same trick works on bitcoin. Verify the full address on the hardware wallet screen, every time, and never copy from history.
Wrench attacks
What it looks like: home invasion, kidnapping, or threats against family to force a transfer. Chainalysis documented 46 attacks and more than $30 million stolen in the first half of 2026, on pace for a record year. The defenses are privacy, keys stored away from home, multisig or time delays, and a plan your family knows.
Malware and clipboard hijackers
What it looks like: a compromised computer swaps the address you paste or captures a seed you type. This is the reason every serious 2026 hardware wallet emphasizes air-gapped signing and on-device address confirmation.
Loss and inheritance failure
What it looks like: a paper backup destroyed, a passphrase forgotten, heirs who cannot find or use the keys. It is the most common outcome we see at the counter. No headline, same result. Steel backups in two locations, a tested restore, and written instructions for your heirs prevent it.
Is it safe to keep bitcoin on an exchange?
Keeping bitcoin on an exchange is a loan to a company, not ownership. It is fine for an amount you are actively trading and wrong for savings you cannot afford to lose.
When your bitcoin sits on an exchange, the exchange holds the keys. You hold an IOU that depends on their security team, their solvency, their regulators, and their willingness to let you withdraw on the day you need to. Exchanges have gotten better since 2022, and most large ones now publish proof-of-reserves attestations. But the largest theft in crypto history, the $1.4 billion Bybit hack of February 2025, hit a major exchange’s own cold storage through a manipulated signing process. The people who lost nothing that day were the ones whose coins were not there.
A practical rule: if an amount would hurt to lose, it belongs in a wallet you control. Everything in the rest of this guide is about doing that safely. If you are starting from zero, our Bitcoin Wallets 101 guide explains the wallet types before you buy anything.
What is the safest way to store bitcoin?
The safest way to store bitcoin for most people is a hardware wallet with a seed you helped randomize, backed up on steel. Add a passphrase as the amount grows, and multisig once a single lost key would really hurt.
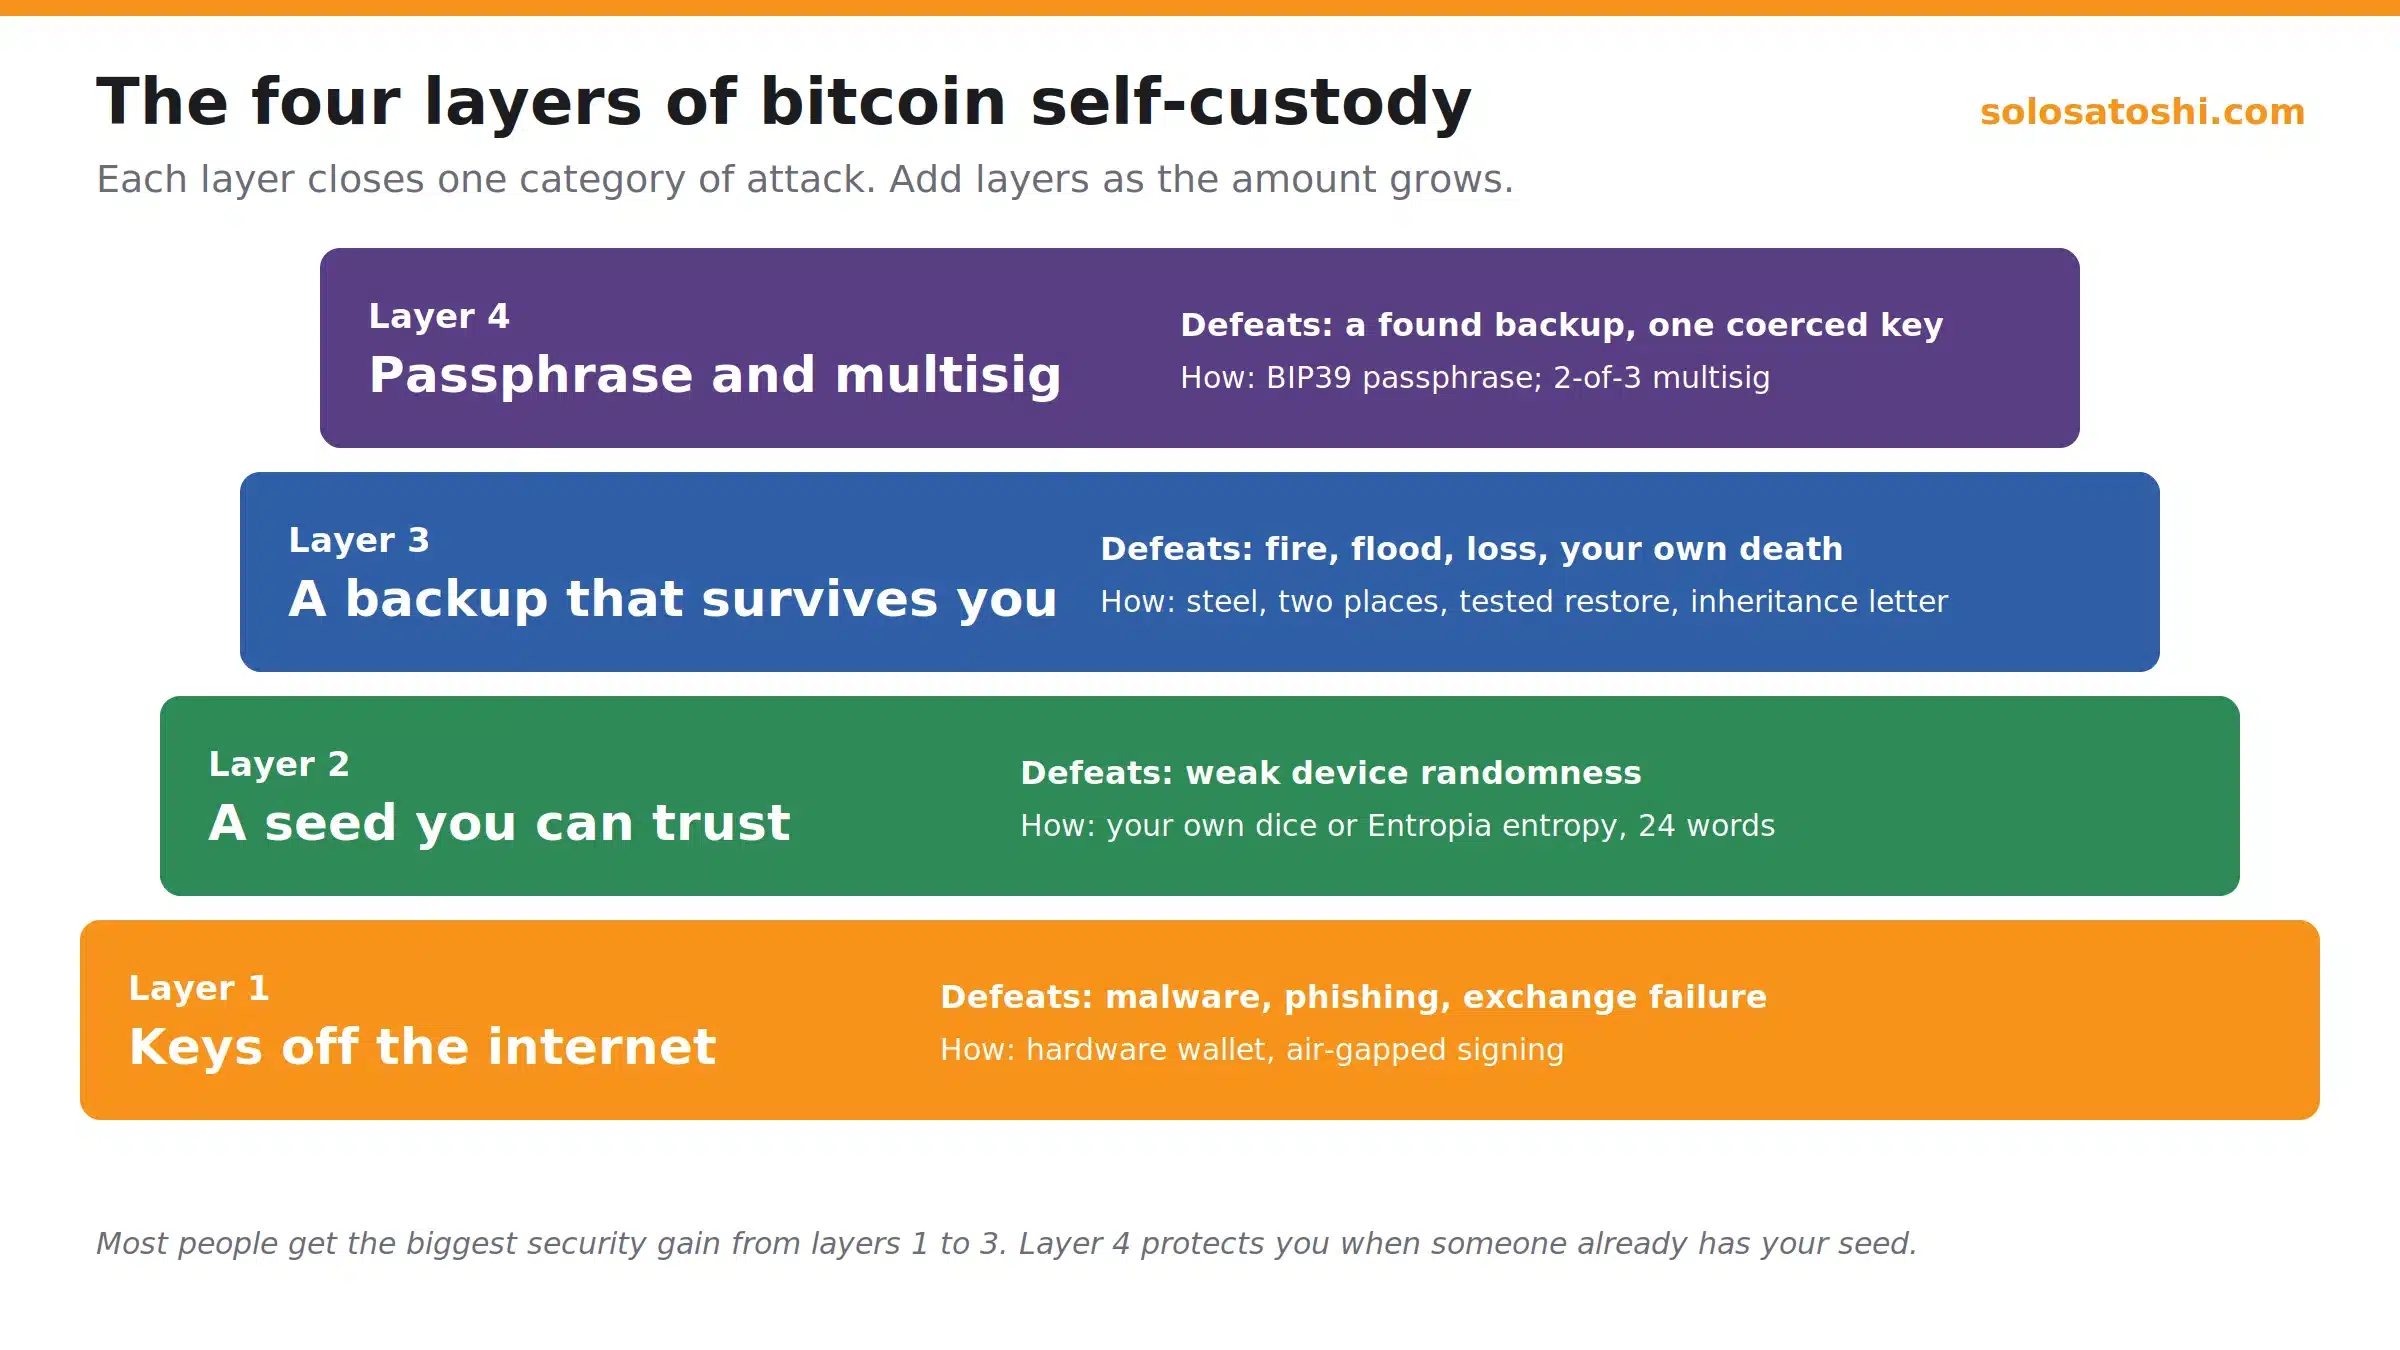
Think of it as layers. Each one closes a category of attack, and you add layers as the value grows.
Layer 1: keys off the internet
A hardware wallet, also called a signing device, holds your private keys on a device that never exposes them to your computer or phone. Transactions are built on the connected device and sent to the signer, which shows you exactly what you are about to sign and signs it internally. Malware on your laptop cannot spend what it cannot see.
Layer 2: a seed you can trust
Your seed phrase is a 12- or 24-word BIP39 encoding of a random number. Every key in the wallet is derived from it. If that random number was weak, the device’s security features are decoration. This is the layer the Coldcard incident exposed, and it is covered in its own section below.
Layer 3: a backup that survives you
Fire, flood, a move, a divorce, a death. Paper fails at all of them. A steel seed phrase backup kit and a second location fix most of them. Written instructions for your heirs fix the rest.
Layer 4: protection against a compromised backup
A BIP39 passphrase creates a second wallet that cannot be reached with the seed words alone. Multisig requires more than one key to spend at all. These are the layers that protect you when someone else has already found your seed.
Most people get the biggest security gain from layers 1 through 3, which cost a weekend afternoon and a few hundred dollars.
How do you choose a hardware wallet in 2026?
Choose a hardware wallet that is bitcoin-only and open source. It should also sign without a USB data connection to your computer, show the full address and amount on its own screen, and let you add your own entropy when creating a seed.
Those five criteria eliminate most of the marketing noise. Bitcoin-only firmware has a smaller attack surface than multi-coin firmware. Open source means the seed-generation path can be audited, which is how the Coldcard bug was found and how Foundation’s CEO Zach Herbert explained the community’s fast response. Air-gapped signing means the device and your computer never share a data connection; they exchange the transaction by QR code or a microSD card, so your computer never has a channel into the device. On-device verification defeats malware and address poisoning. User-supplied entropy defeats the next RNG (random number generator) bug nobody has found yet.
| Device | Keeps a seed on it? | Best fit |
|---|---|---|
| SeedSigner+ | No (stateless) | Most private; nothing to steal |
| Blockstream Jade Plus | Yes, PIN-protected | Easiest guided setup |
| Foundation Passport Prime | Yes, secure element | Larger holdings; premium |
SeedSigner+
QR only: no USB data, no Bluetooth, no Wi-Fi. It generates seeds from 99 rolls of a six-sided die or a camera image, and can take 11 or 23 words and calculate the last one. It is stateless, meaning it stores nothing. You load the seed from a SeedQR or type it each session, and it is forgotten at power-off, so there is nothing on the device for a thief to take.
Blockstream Jade Plus
Signs by scanning QR codes with its camera, or fully air-gapped with the JadeLink USB storage; USB and Bluetooth are optional. When it creates a seed it mixes your button presses, sensor noise, and its hardware random number generator. It also accepts 11 or 23 words you drew yourself and calculates the checksum word, and it supports Blockstream’s two-d16-plus-d8 dice method. The seed is stored on the device behind a PIN, with an optional stateless mode using a SeedQR (your seed printed as a QR code you scan each session).
Foundation Passport Prime
Signs by QR camera or microSD card, with no USB data connection required. The seed comes from three independent hardware sources, and since KeyOS 1.3.1 it accepts 11 or 23 words you drew and calculates the final word. The seed is stored behind a PIN in a secure element, a separate chip designed to resist physical tampering.
Each device is also sold as a complete starter kit with steel backup, dice, and tamper-evident bags. Those kits are ranked in the next section.
Where to buy hardware, and why it matters
Buy hardware wallets from the manufacturer or an authorized retailer, never from a third-party marketplace listing or a “sealed, never opened” resale. Tampered devices with pre-generated seeds and printed “your recovery words” cards are a known scam. When your device arrives, it should ask you to create a new seed; if any seed words are printed in the box, do not use them.
What is the best starter kit for self-custody?
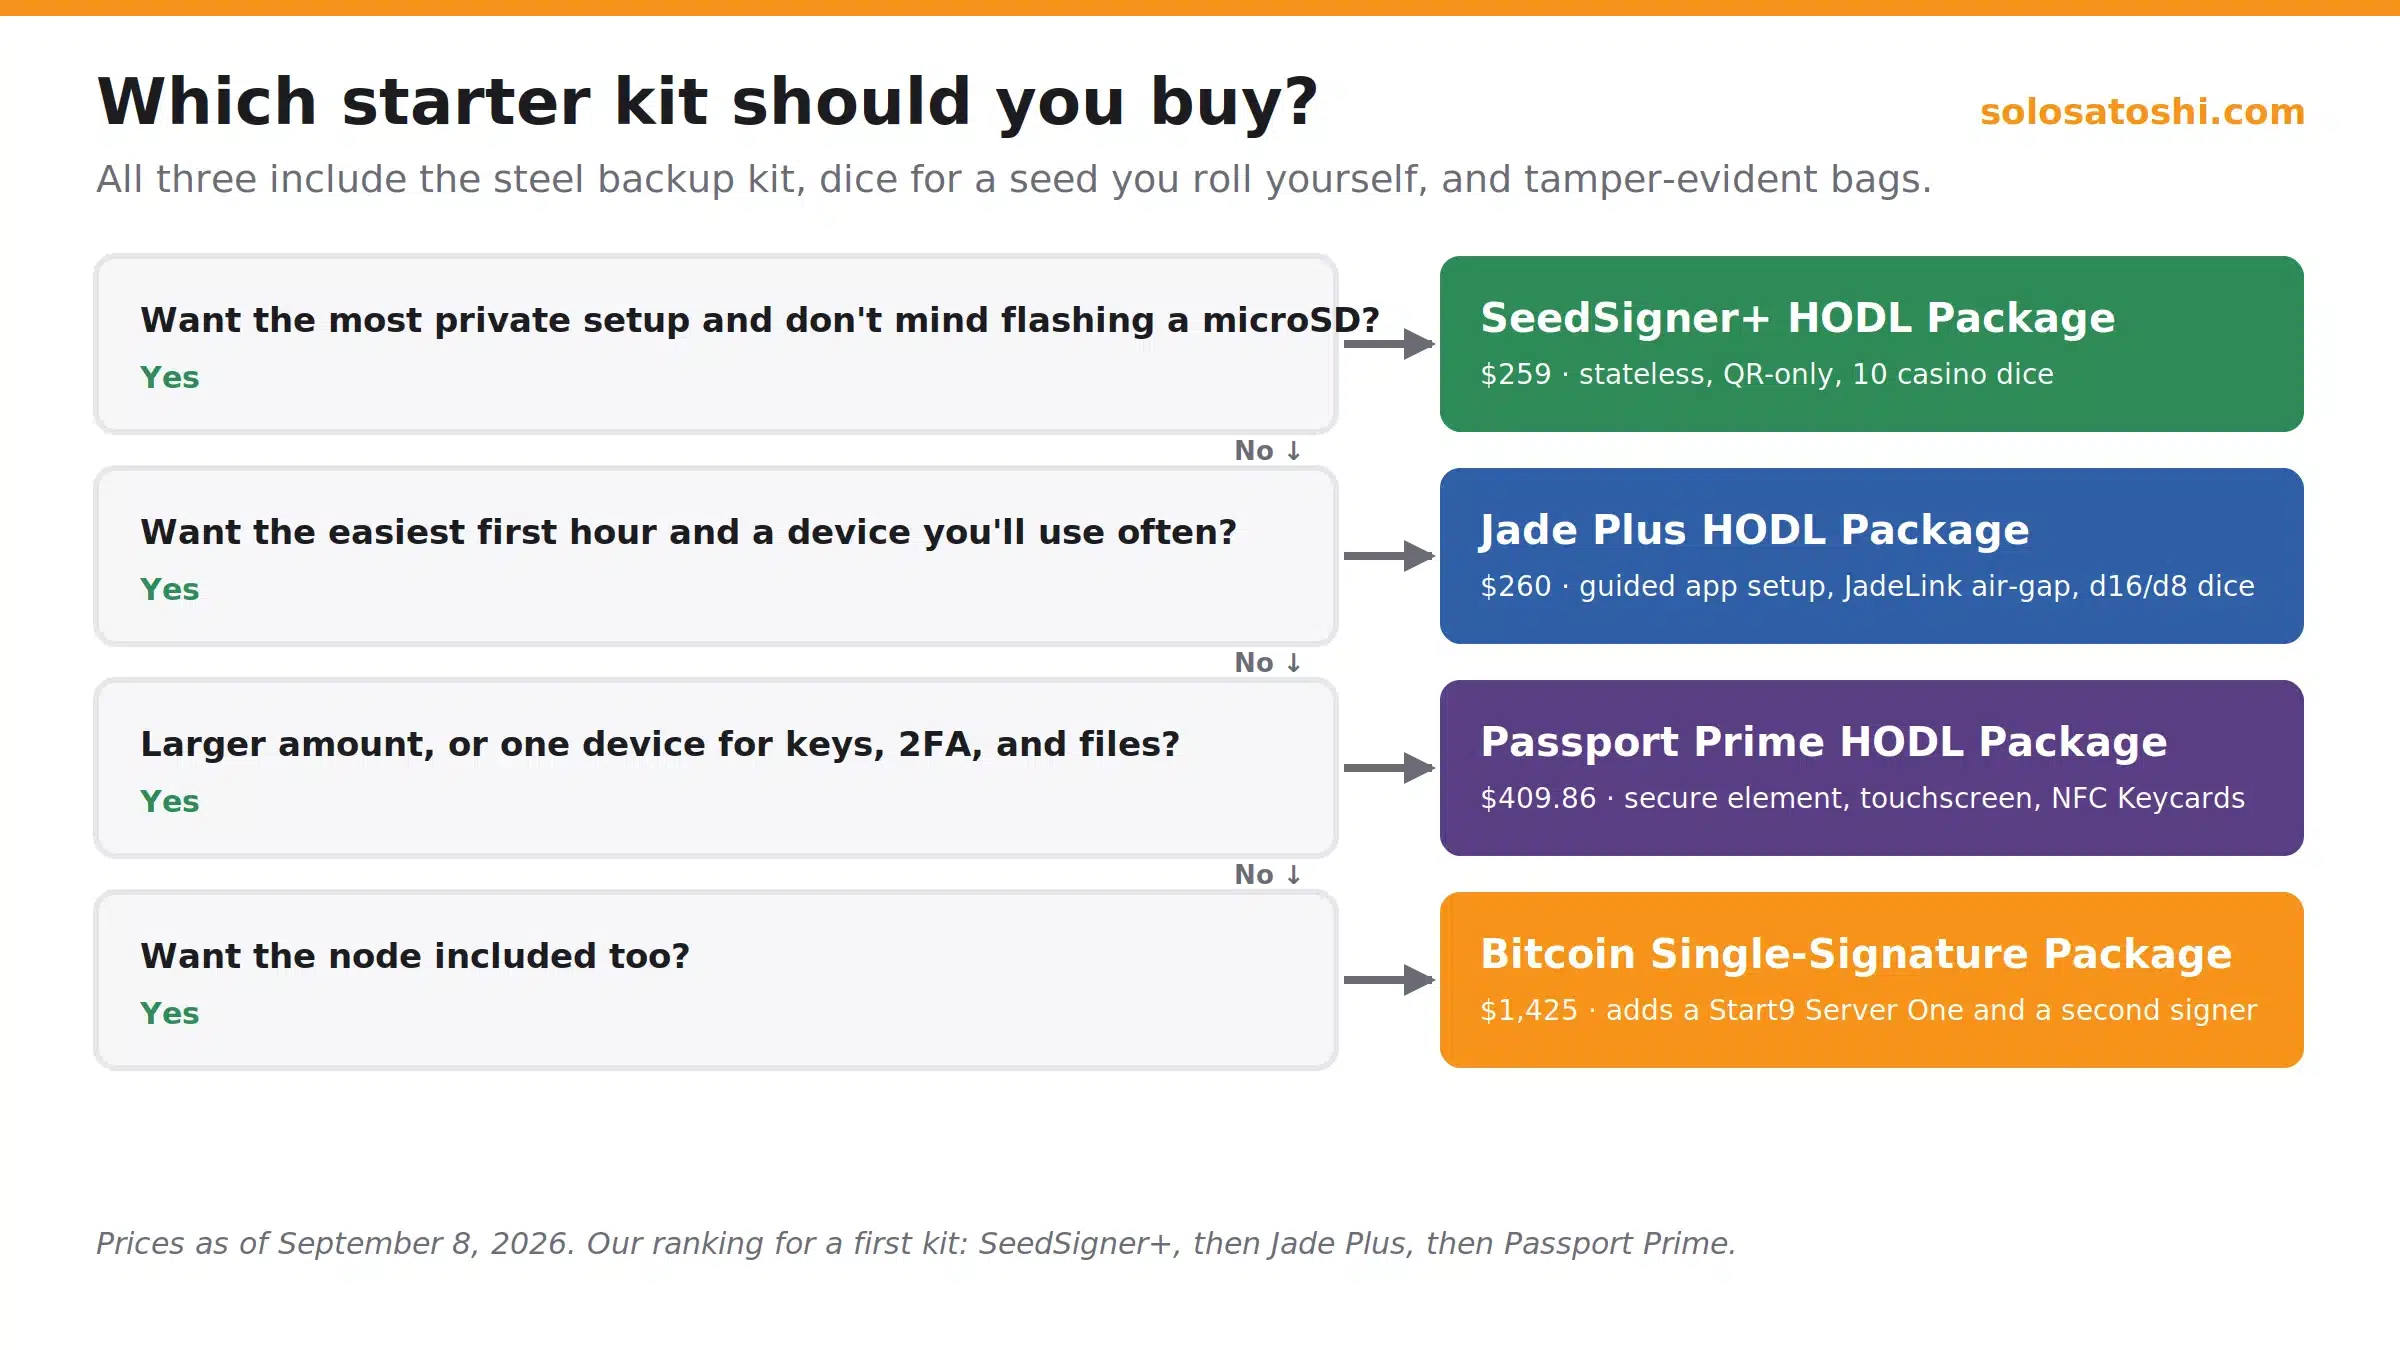
The best starter kit for most people is the SeedSigner+ HODL Package, followed by the Jade Plus HODL Package, then the Passport Prime HODL Package. All three ship with the same steel backup kit, dice for a seed you roll yourself, and tamper-evident bags, so a beginner gets every layer in one box instead of piecing it together.
That is our ranking, not a spec-sheet result. It comes from what we watch customers succeed with at the counter. Every kit below includes the three-plate Bitcoin Seed Phrase Backup Kit with electric engraving pen and four tamper-proof seal bags. What changes is the signer and the dice.
| Rank | Kit | Price |
|---|---|---|
| 1 | SeedSigner+ HODL Package | $259 |
| 2 | Jade Plus HODL Package | $260 |
| 3 | Passport Prime HODL Package | $409.86 |
1. SeedSigner+ HODL Package
In the box: SeedSigner+ (assembled in the USA, no Wi-Fi or Bluetooth hardware, power-only USB-C), a blank microSD card, ten casino-grade six-sided dice, the steel backup kit, and four seal bags.
Why it is first: it is the only signer here that stores nothing. The seed lives only in memory while you use it and is gone at power-off, so a lost or stolen device gives an attacker nothing; your steel plates are the wallet. It talks to your computer by QR code only. Ten casino dice mean a 24-word seed is ten throws, entered straight into the device, no lookup table. It is also the natural second key when you graduate to multisig.
Honest trade-off: the microSD ships blank, so you download, verify, and flash the SeedSigner software yourself before first use. That is by design (you trust the project’s signed release, not the supplied microSD card), and the included setup card walks you through it, but it is one more step than the other two kits. You also load the seed each session from a SeedQR or by typing it, which some people find tedious for frequent use.
2. Jade Plus HODL Package
In the box: Blockstream Jade Plus in Lunar Silver metal (camera, battery, Genuine Check on first boot), a JadeLink USB-C drive for fully offline signing and firmware updates, two sixteen-sided dice and one eight-sided die, the steel backup kit, and four seal bags.
Why it is second: the most guided setup of the three. The Blockstream app walks you through creating a wallet on a phone or laptop, the Jade stores the seed behind a PIN so daily use is fast, and the JadeLink lets you keep it air-gapped anyway. The dice set produces one seed word per throw using Blockstream’s published table, and the Jade calculates the final word. If you want the same workflow for less, the original plastic Blockstream Jade runs the same firmware without the metal body, battery, or JadeLink.
Honest trade-off: the seed is stored on the device (encrypted, PIN-locked, with Blockstream’s open-source blind-oracle scheme rather than a traditional secure element), so a stolen Jade is something to react to, which is what the seal bags and PIN are for.
3. Passport Prime HODL Package
In the box: Foundation Passport Prime (3.5-inch touchscreen, secure element with active anti-tamper, QR camera, assembled in New Hampshire), three NFC Keycards with Faraday sleeves for an encrypted 2-of-3 backup of the master key, two sixteen-sided dice and one eight-sided die, the steel backup kit, and four seal bags.
Why it is third: not because it is weaker. It is the most premium device here, with the best screen for reading a full address, a hardware secure element, and extras (2FA codes, FIDO security keys, encrypted file vault) that consolidate several devices into one. It ranks third for a starter because it costs $150 more and does more than a first-time holder needs. If you are protecting a larger amount from day one, or you want one device for keys, logins, and files, start here.
Honest trade-off: price, and more features means more to learn. The Keycard backup is convenient, but treat the steel plates as the backup of record.
Which one should you buy?
- Want the most private setup and don’t mind flashing a card: SeedSigner+.
- Want the easiest first hour and a device you will use often: Jade Plus (or the classic Jade on a budget).
- Holding a larger amount or want one device for keys, 2FA, and files: Passport Prime.
How do you generate a seed phrase that cannot be brute-forced?
Generate your seed by mixing the device’s random number generator with randomness you produced yourself. For a 24-word seed that means 99 rolls of a six-sided die, 64 rolls of a sixteen-sided die, or 23 draws from a set of Entropia v2 tablets.
The reason is simple. Mixing entropy sources can only make a seed stronger. If the device RNG is perfect and your dice are slightly biased, the result is still perfect. If your dice are fair and the device RNG is broken, the result is still perfect. You only lose if both fail at once.
That is not a hypothetical. From March 2021 until July 2026, a build error in Coldcard firmware caused seed generation to fall back to a general-purpose software PRNG instead of the chip’s hardware random number generator. Coinkite’s own technical backgrounder estimates the effective search space at about 40 bits on Mk2 and Mk3 devices and about 72 bits on Mk4, Mk5, and Q, instead of the intended 128. Beginning July 30, 2026, attackers swept roughly 1,367 BTC (about $89 million) from more than 4,500 addresses in three days, and later tallies pushed the total past $110 million. The devices were never touched. The seeds were simply guessed.
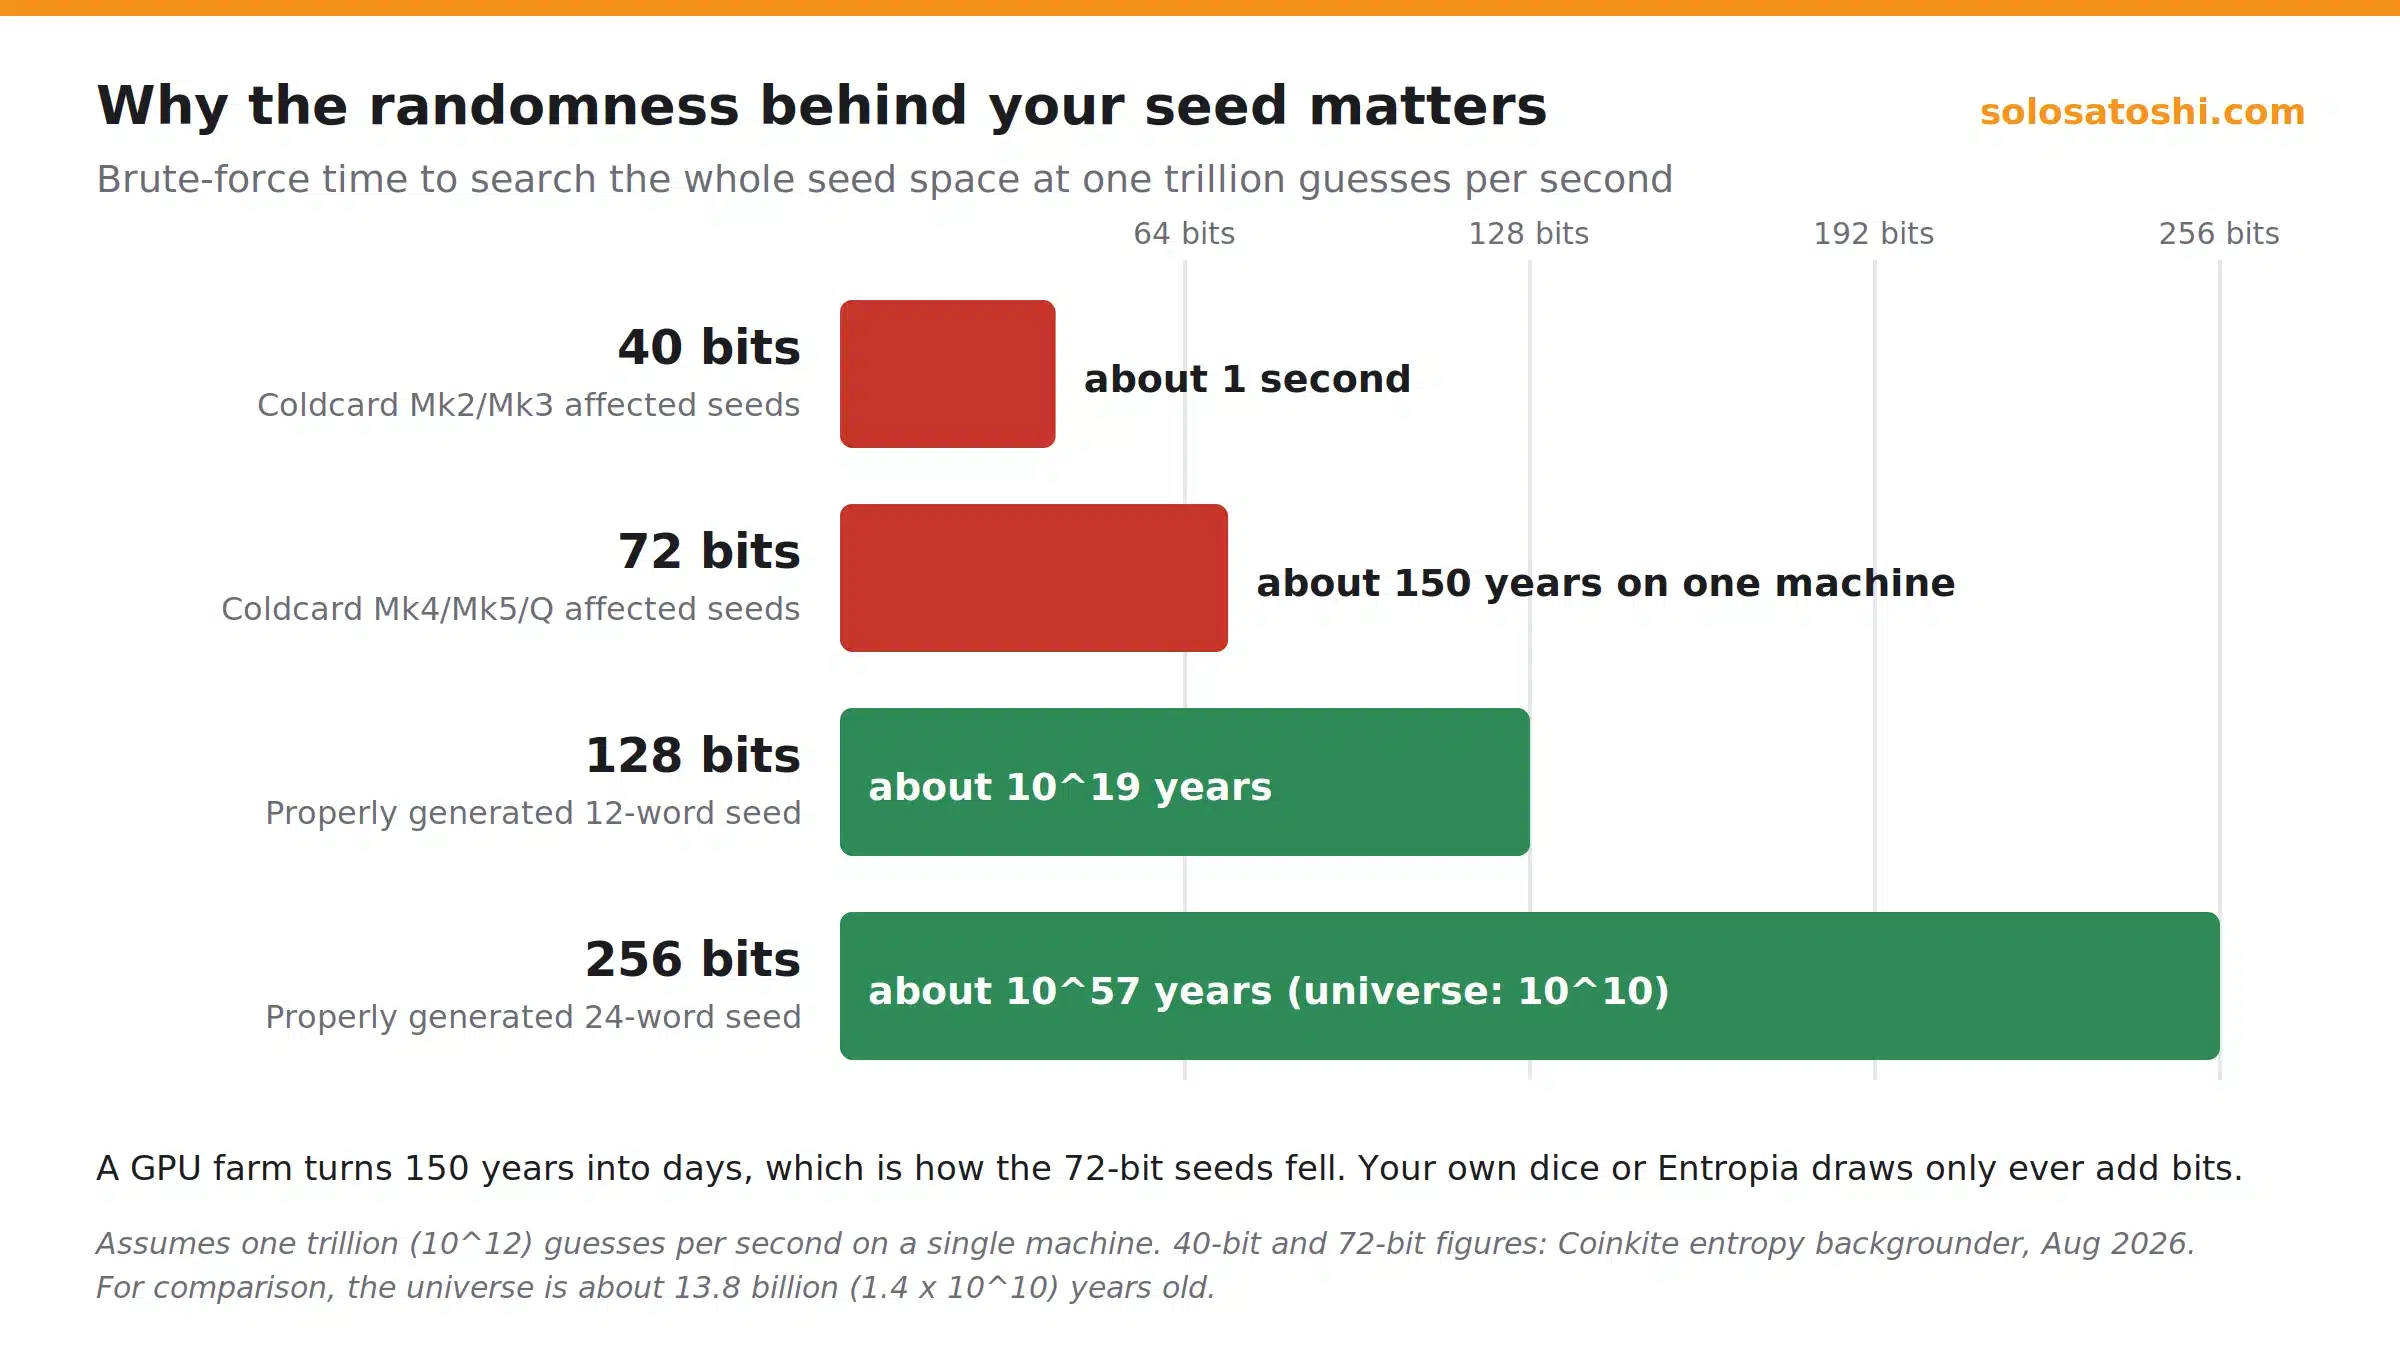
Two groups of Coldcard owners were not at risk: users who had entered at least 50 of their own dice rolls at seed creation, and users with a strong, unique passphrase. Coinkite has since made user entropy mandatory for every new seed. We think that should be the standard for every wallet. There are three ways to do it, and none needs a computer. All three kits below are the same ones we pack into our HODL packages; the times are from our own bench.
| Kit | 24-word seed | Price |
|---|---|---|
| Casino d6 dice set (5 dice) | 20 throws, ~11 min | $19.99 |
| Two d16 + one d8 dice set | 23 throws, ~22 min | $9.99 |
| Entropia v2 tablets | 23 draws, ~14 min | $49.99 |
Which kit for which wallet
- Casino d6 set. Five Grade AAA precision dice, serialized as a matched set, so back-filled pips keep every face equally likely. Roll all five at once and enter the digits: 20 throws covers 99 rolls. Native on the SeedSigner+ (Tools, then Dice) and on Coldcard; the device hashes the rolls into the seed for you.
- Two d16 + one d8 set. One throw of all three gives 2,048 outcomes, which is exactly one BIP39 word. Look it up in Blockstream’s printed table, write it down, repeat 23 times, and let the Jade Plus, SeedSigner+, or Passport Prime calculate the final word. Numbered faces, so nothing to convert.
- Entropia v2. 1,024 double-sided tablets, one face per BIP39 word. Draw from a bowl, record the word, put it back. The words you draw are the seed, so there is nothing to hash and nothing to trust. Fastest of the no-conversion methods on our bench.
The full walkthrough for every method, with a tablet fairness test and the d6 roll count math, is in Seed Phrase Entropy Explained.
If you already hold bitcoin on a seed you did not add entropy to, you do not need to move it tonight. Your next wallet should be built this way, and if any seed came from an affected Coldcard, replace it now and migrate.
How should you back up your seed phrase?
Back up your seed phrase on stamped or engraved steel, in at least two locations you control, and never in digital form. Then prove the backup works by wiping the device and restoring from it before you send real funds.
The steel backup is the part people skip because paper feels fine on day one. Paper is not fine in year five or in a natural disaster.
Rules that prevent the common disasters
- No photos, no cloud, no password manager, no notes app. A seed that has ever touched a networked device should be considered exposed. The $282 million January theft started with a backup being shared.
- Two locations, not two copies in one drawer. Home and a safe-deposit box, or home and a trusted relative’s safe. Fire takes out one; it should not take out both.
- Do not split a single seed across locations. Six words here and six words there cuts your security in half if either half is found. If you want to split, use multisig, which is designed for it.
- Label the backup with the wallet fingerprint, not your name. The fingerprint (a short hex code your signer shows you) lets you confirm you restored the right seed years later without identifying whose it is.
- Test the restore. Wipe the device, enter the words from the steel, confirm the fingerprint and first receive address match what you wrote down, then send a small test amount before the rest.
- Write an inheritance letter. Where the backups are, what device to use, what the passphrase is (stored separately), and who to call for help. Seal it with your will.
Should you add a passphrase?
Add a passphrase once you hold more bitcoin than you would be comfortable losing to a found backup. It creates a hidden wallet the 24 words alone cannot open, but it is also a second thing you can lose.
A passphrase (sometimes called a 25th word) is any text you choose, mixed with your seed to produce a different set of keys. A thief who finds your steel plate finds an empty wallet. That protection is real: Coinkite confirmed that affected Coldcard seeds protected by a strong, unique passphrase were not immediately exposed in the July sweeps.
The trade-off is unforgiving. Every passphrase, including one with a typo, opens a valid, empty wallet with no error message. Forget it and the coins are gone. If you use one:
- Make it long and unique: a random sentence or several unrelated words, not a birthday or a quote.
- Back it up in steel, in a different location from the seed words.
- Verify the fingerprint after entering it, every time, before you deposit.
- Put it in your inheritance letter. A passphrase your heirs cannot find is a donation to no one.
A passphrase is a second factor, not a fix for a weak first factor. It does not repair a seed generated with bad entropy.
When does multisig make sense?
Multisig makes sense when a single lost or stolen key would be a life-changing loss. Below that point, the cost of managing two or three devices and their backups usually outweighs the benefit.
In a 2-of-3 multisig wallet, spending requires signatures from any two of three keys. One key can be stolen, lost, or coerced out of you, and the coins do not move. It is the strongest defense against the wrench attack, because you can honestly tell an attacker that the funds cannot be spent from your home, and it removes the single point of failure that every single-signature setup has.
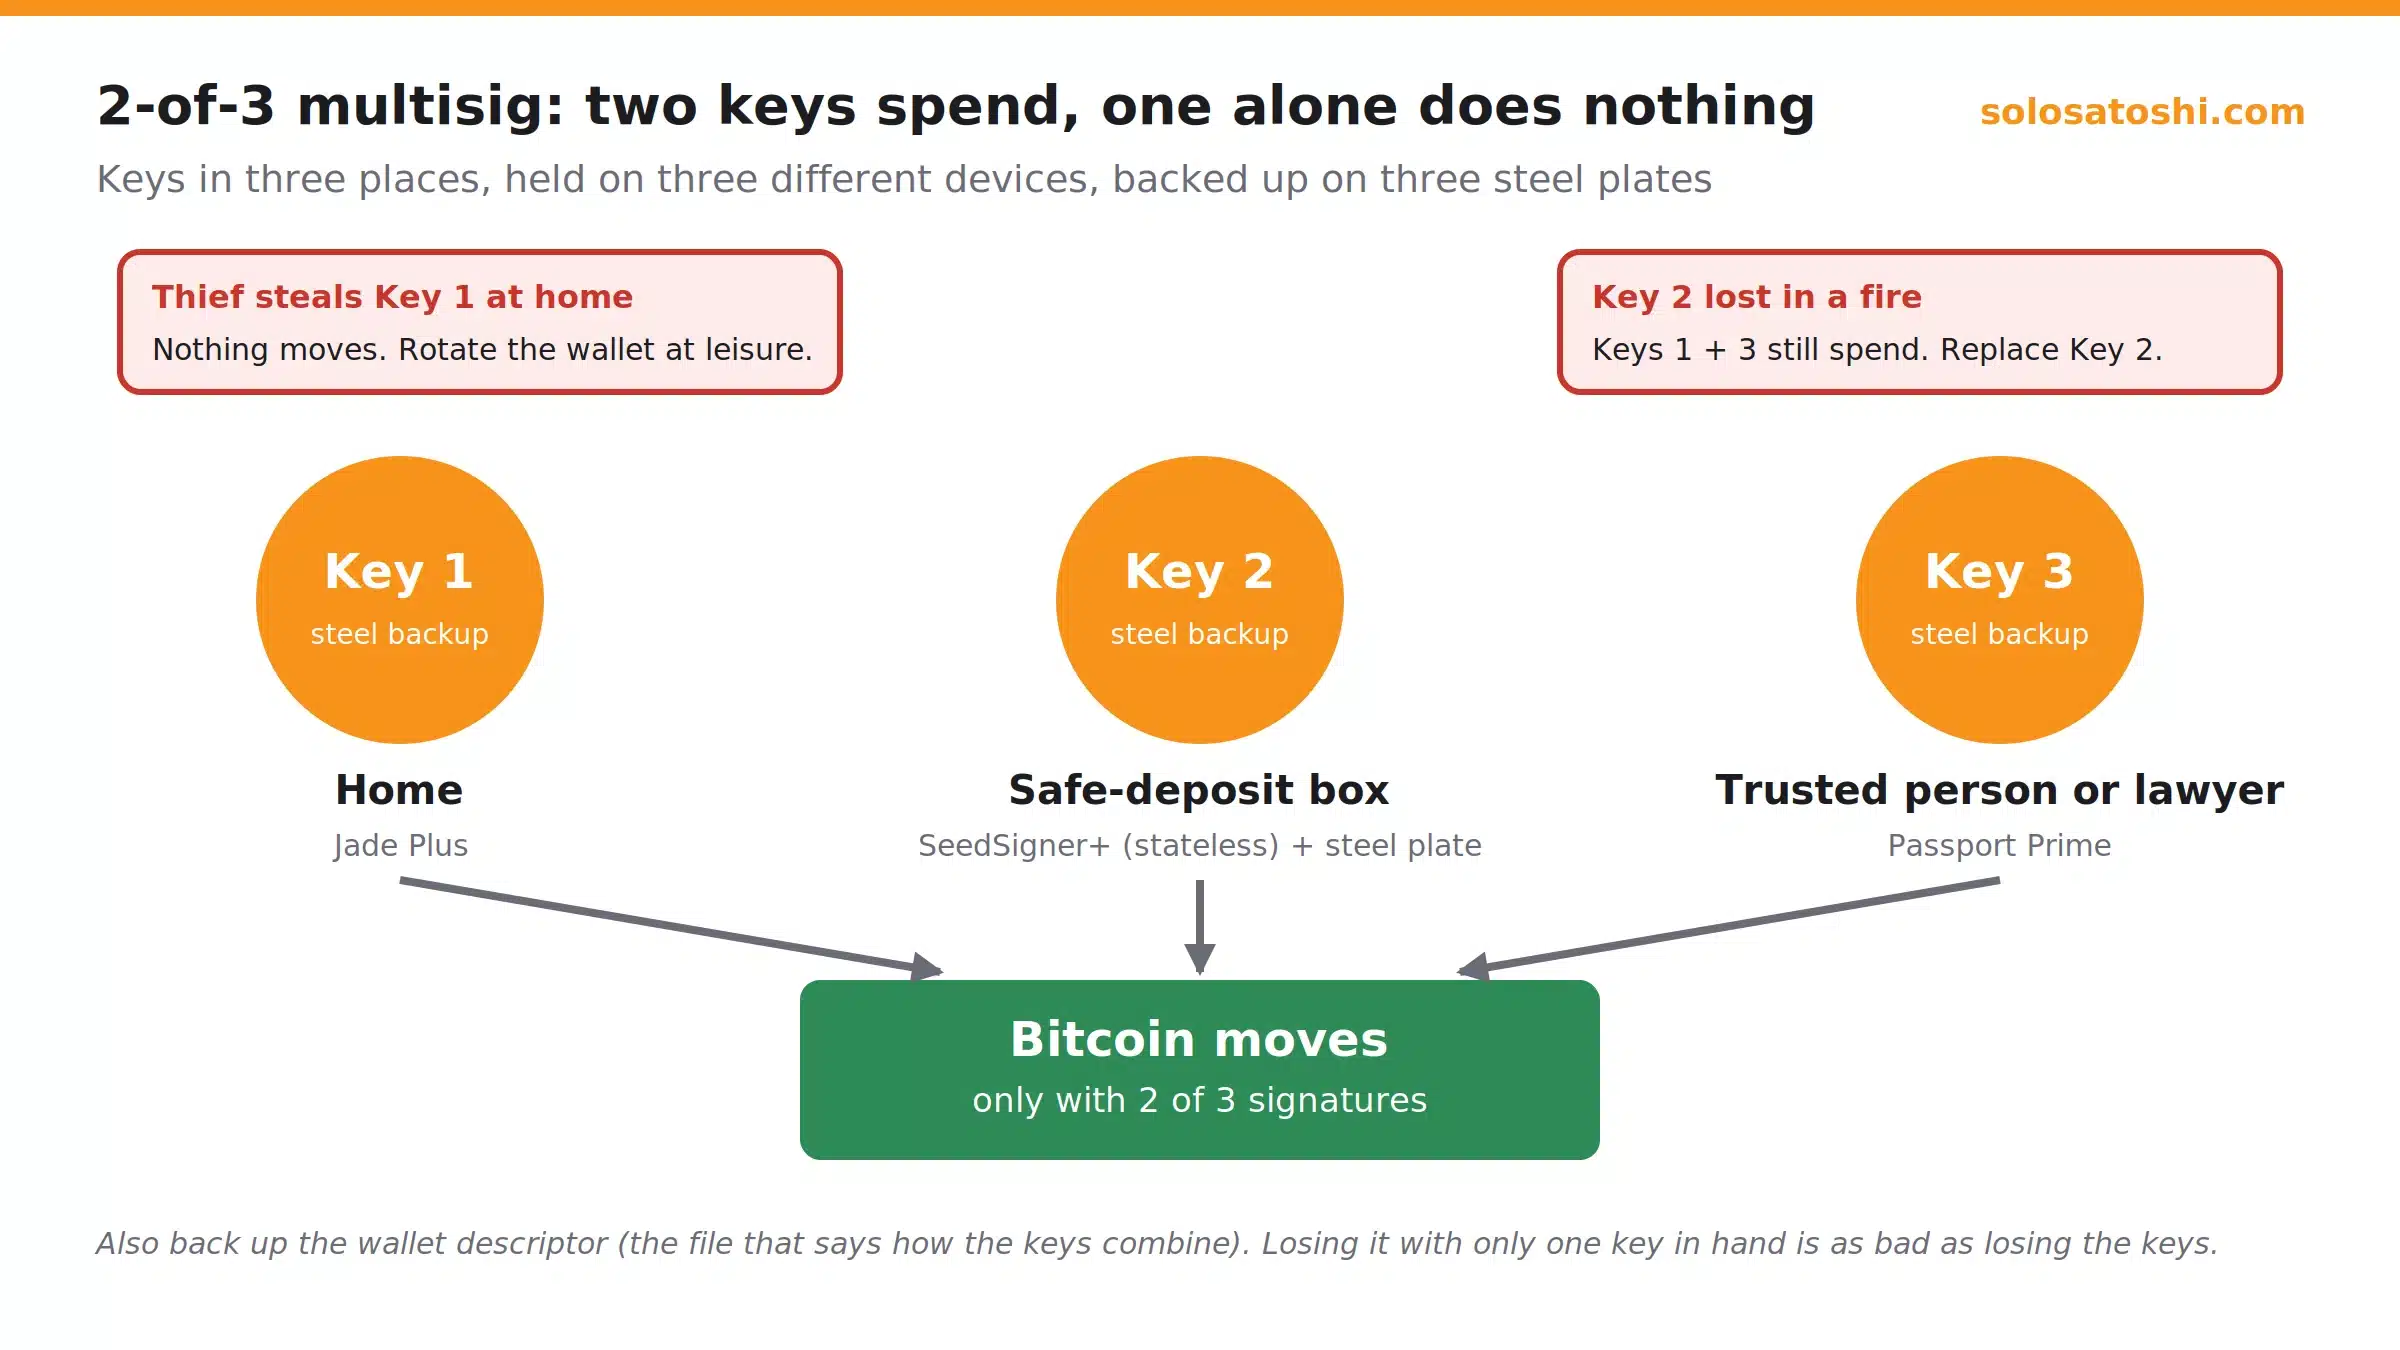
The costs are real: three devices, three steel backups, and a wallet descriptor (the file that tells wallet software how the keys combine) that must be backed up alongside them. Losing the descriptor with only one key in hand is as bad as losing the keys. The setup takes an evening rather than an hour, and recovery drills matter more.
Our advice is to master single-signature first, then upgrade. Mixing device vendors is the point of multisig, which is why our Bitcoin Multi-Signature Package pairs the Jade Plus, SeedSigner+, and Passport Prime with a Start9 node, and the Multi-Signature Upgrade adds the extra signers to a single-sig kit you already own.
How do you avoid phishing, fake support, and address poisoning?
Treat any contact that asks for your seed, your PIN, or a “wallet verification” as an attack. Defeat address poisoning by reading the full receive address on your hardware wallet’s screen instead of copying it from your transaction history.
The January 10, 2026 theft is the template. According to on-chain investigator ZachXBT and security firm ZeroShadow, as reported by CoinDesk, the attacker posed as support for a well-known hardware wallet vendor and convinced the victim to share their wallet backup. There was no exploit, no malware, and no flaw in the device. Once the seed was out, 1,459 BTC and 2.05 million LTC moved in one night, most of it swapped to Monero within days.
The rules that would have prevented it
- No company will ever ask for your seed phrase. Not to “verify,” not to “migrate,” not to “protect you from a breach.” If someone does, they are the breach.Assume your contact details are public.
- Wallet vendors, exchanges, shipping partners, and tax services have all leaked customer lists, and attackers now use AI to join those leaks into one profile and write the phish. A scammer knowing which wallet you own proves nothing.
- Never install “support” software or share your screen. The $243 million theft of August 2024 used a screen-share tool; the pattern has not changed.
- Type URLs; do not click them. Bookmark the manufacturer’s or authorized retailers site and your wallet software’s download page.
- Verify firmware updates on the manufacturer’s site. Never from a link in an email, DM, or search ad.
Address poisoning, and why “send a test transaction” is no longer enough
Address poisoning works by sending you dust (a tiny, worthless amount) from an address whose first and last characters match one you have used before, so that the fake appears in your history looking like the real one. On January 31, 2026, one user copied the wrong entry and lost 4,556 ETH, about $12 million, in a single transaction. Attackers now watch the mempool (the public waiting room for unconfirmed transactions) for small test sends and poison histories immediately afterward, so a test transaction followed by copying from history can make it worse.
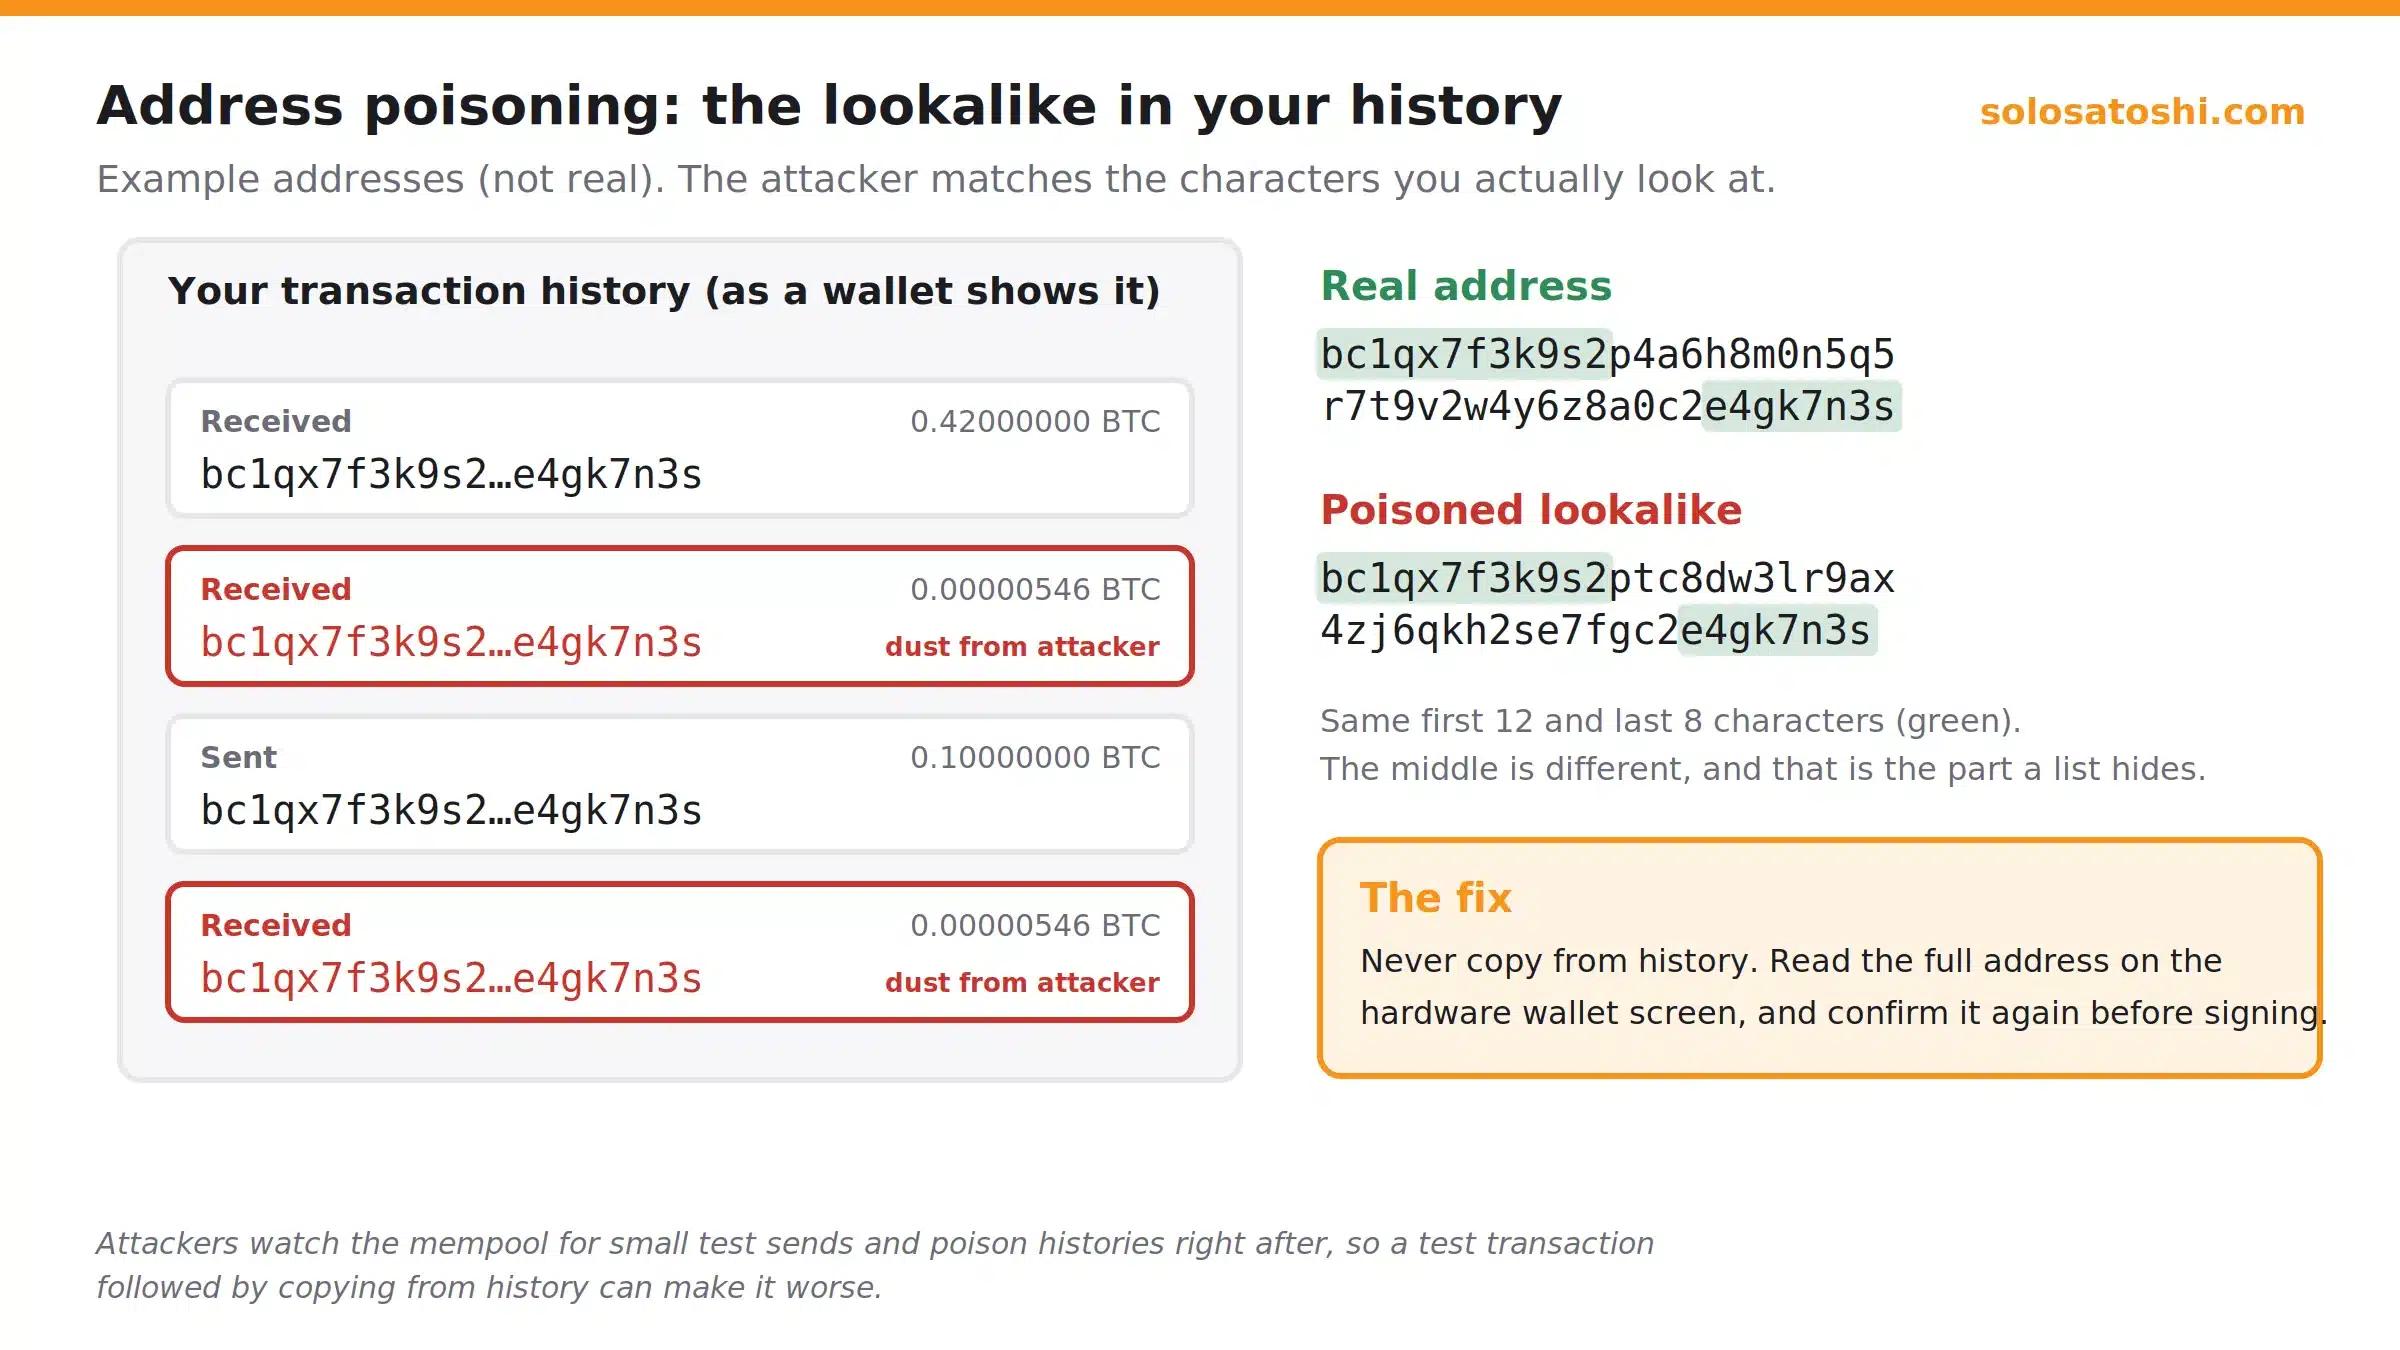
The fix is procedural. Get the receive address from the signing device’s screen, compare the entire string (not the first and last four characters) against what your wallet software shows, and confirm the full address and amount on the device again before signing a send. It takes thirty seconds. It is the only thing that has stopped every version of this attack.
How do you protect yourself from wrench attacks?
Protect yourself from wrench attacks by keeping your holdings private and keeping keys and backups out of the home where possible. Use multisig or a decoy wallet so no single confrontation can move the coins, and make sure your family knows the plan.
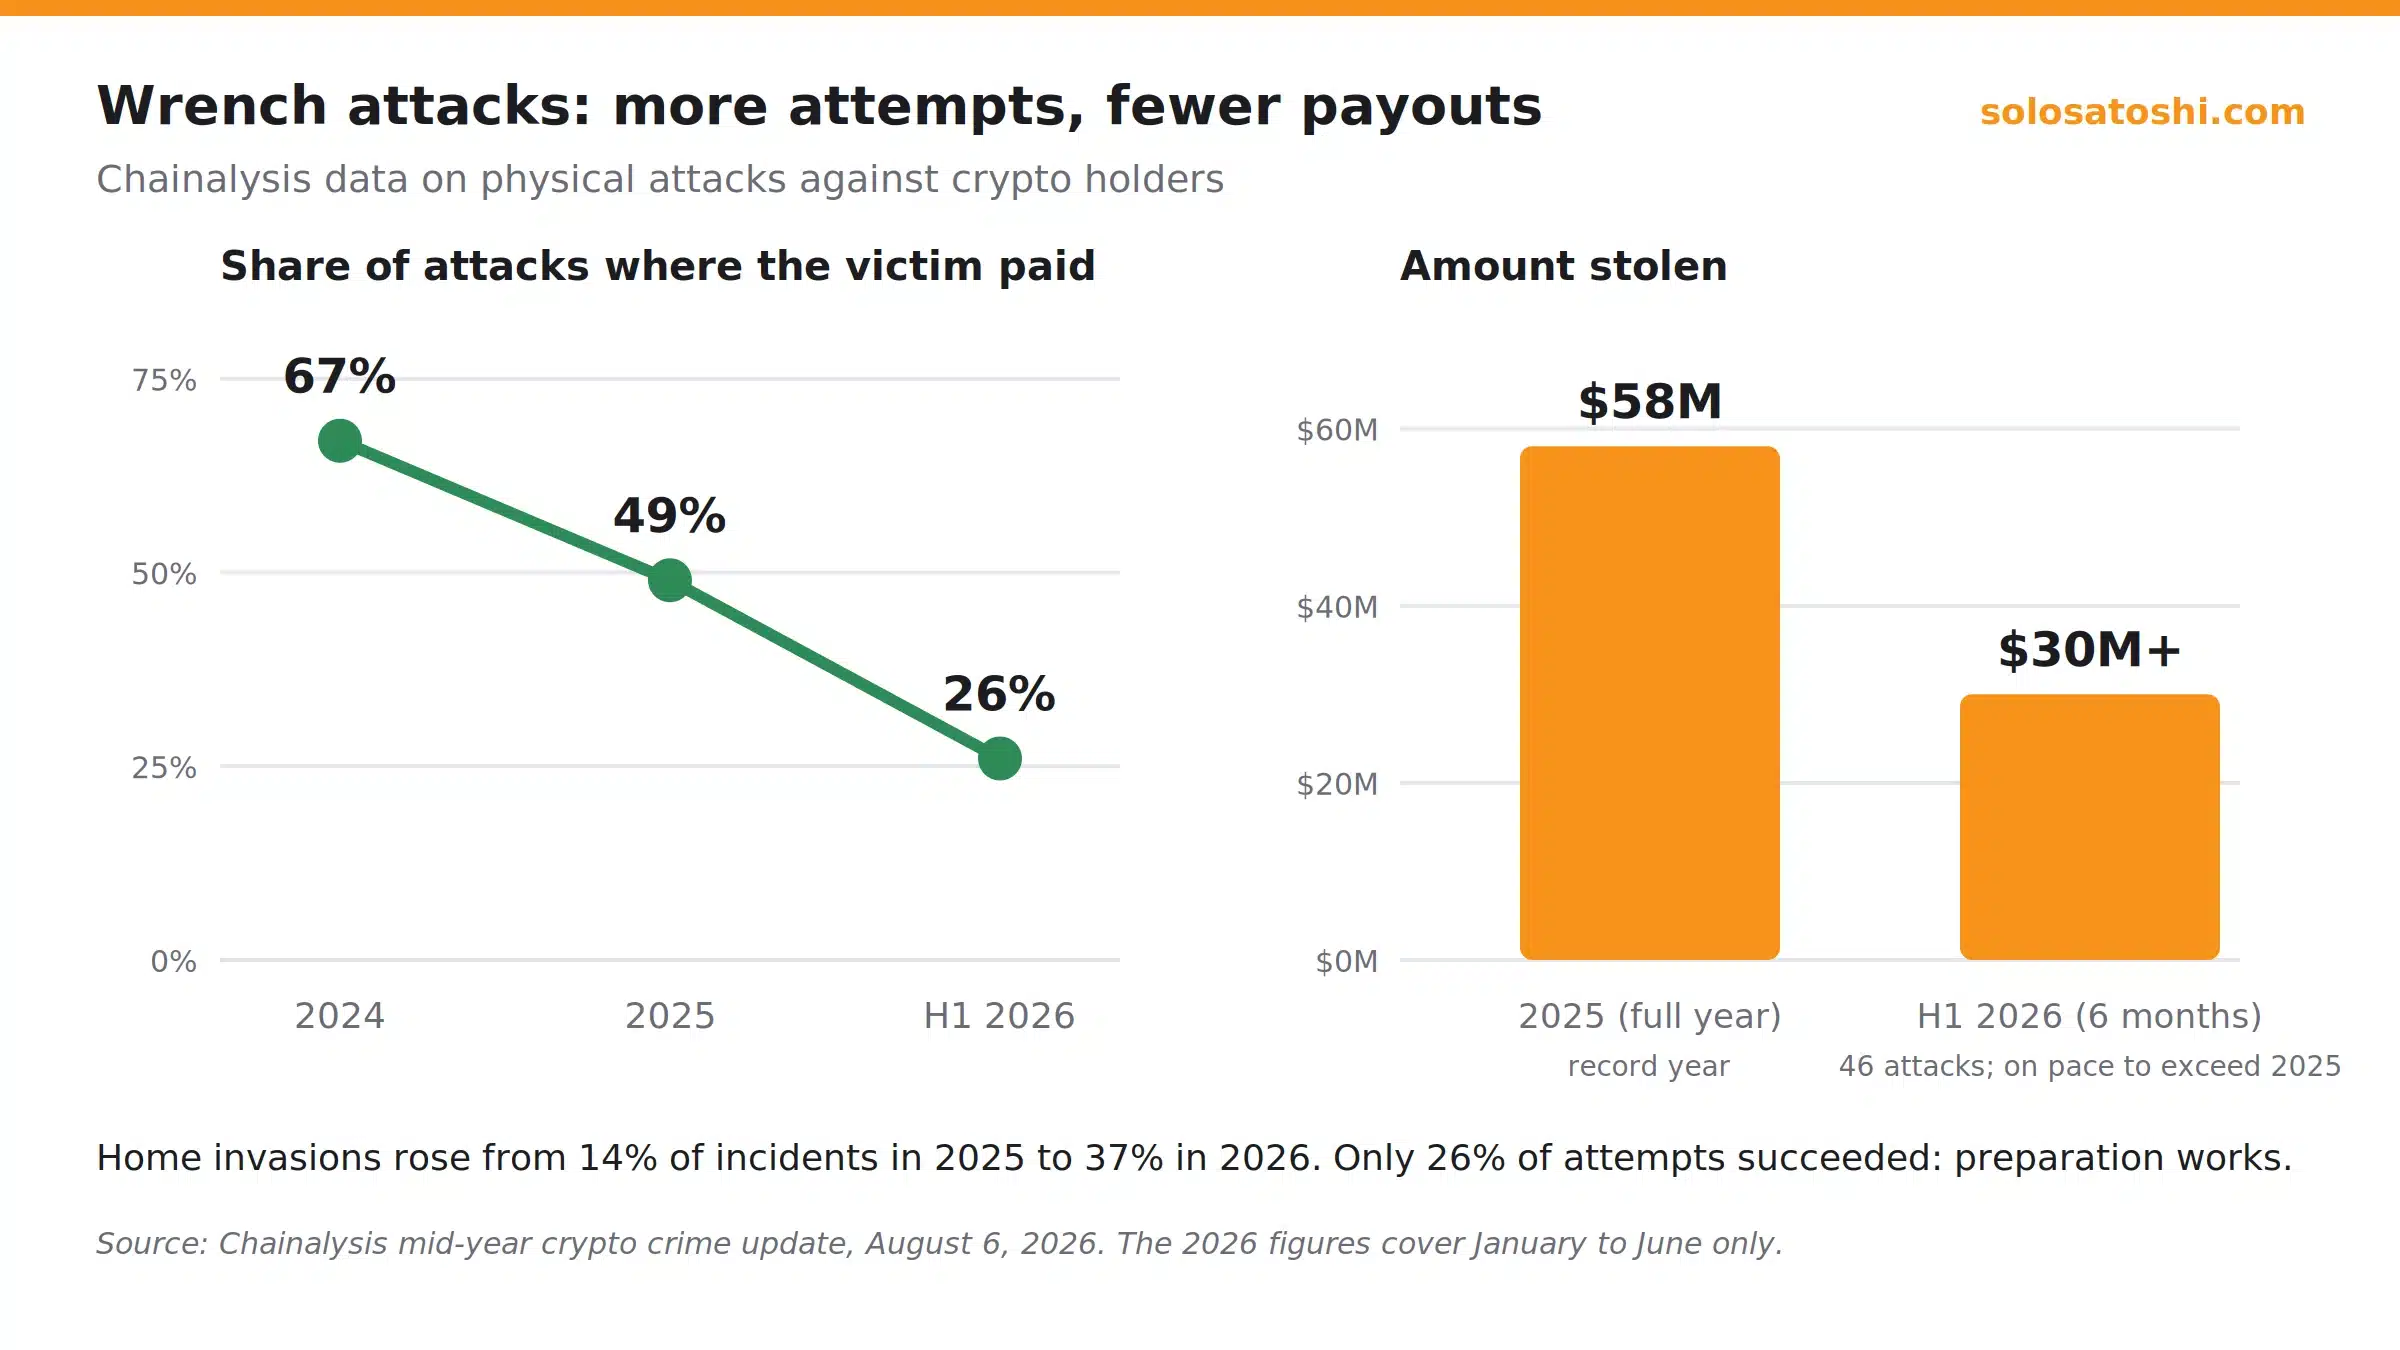
The numbers changed this year. Chainalysis’s mid-year update documented 46 violent attacks on crypto holders in the first half of 2026 and estimated more than $30 million stolen, on pace to beat 2025’s record of about $58 million. Home invasions rose from 14% of incidents in 2025 to 37% this year, and family members or acquaintances were targets in roughly 25% to 30% of cases. France recorded 30 incidents, and Chainalysis links the surge there to leaked tax and customer records, which is a reminder that your data is only as private as the least careful company that holds it.
One number offers hope: only 26% of attempts resulted in payment, down from 67% in 2024. Preparation works.
Practical defenses
- Do not talk about it. Not at the bar, not on social media, not on a profile that links to your name. This is the single most effective control and it is free.
- Separate the seed from the home. If the backup that opens your main wallet is in a safe-deposit box or with a trusted person hours away, no amount of pressure at your front door can move the coins tonight. Attackers know this; it is why home invasions target holders whose keys are on site.
- Use multisig for the bulk. A 2-of-3 with keys in different places is the honest “I cannot do that from here.”
- Keep a plausible spending wallet. A modest balance on your phone or a single-sig device at home gives you something to hand over. Do not lie about a wallet that does not exist; give up the one that does.
- Reduce your data footprint. Ship hardware to a business address or a PO box, use a unique email for bitcoin services, and assume any KYC exchange (one that verified your identity) you have used has your name, address, and approximate balance in a database somewhere.
- Tell your family the plan. Who not to open the door for, what to hand over, and that no amount of bitcoin is worth resisting a physical threat.
Why does running your own node protect your bitcoin?
Running your own node lets you check your balance and transactions against the blockchain yourself. Without one, your wallet app sends your addresses, balance, and IP address to a company’s server every time you open it.
Most wallet apps connect to a server run by the wallet company. That server learns every address you own, when you check them, and from where. That is a privacy leak at best and a target list at worst. A node at home answers those queries locally. It also means you are not trusting anyone else’s copy of the rules: your node rejects invalid blocks and transactions on its own.
Plug-and-play nodes make this a fifteen-minute job. The Start9 Server One runs Bitcoin Core and an Electrum server (the piece wallet apps connect to) you can point any of the three signers at, and it is included in both of our self-custody packages. Our guide to why to run a Bitcoin node covers the setup.
Is bitcoin safe from quantum computers?
Bitcoin is safe from quantum computers today, because no machine exists that can break its keys. The one practical step for a holder is to avoid reusing addresses, so your public key is never exposed on-chain before you spend.
How hard is a bitcoin key to crack with normal computers?
A bitcoin private key is a 256-bit number, which means there are 2256 possible keys: about 1.16 × 1077, or 116 followed by 75 zeros. For scale, the number of atoms in the observable universe is usually put around 1080. The best known classical attack on Bitcoin’s curve does not need to try every key; it needs roughly 2128 operations, about 3.4 × 1038. Even that is out of reach. A machine making a trillion trillion guesses per second (1024) would need about 3.4 × 10¹⁴ seconds, roughly 11 million years, to find one key. The naive 2256 search at the same speed takes about 1045 years; the universe is about 1.4 × 10¹⁰ years old. Nobody is brute-forcing a properly generated seed, which is why the Coldcard losses happened: those seeds had only 40 to 72 bits of real randomness, not 256.
How much quantum power would it take?
A quantum computer running Shor’s algorithm changes the math, but only against a public key that has been revealed. The question is how many error-corrected qubits it takes, and the estimates keep falling as researchers find shortcuts.
| Estimate | Physical qubits | Time per key |
|---|---|---|
| Webber et al., 2022 | ~317 million | 1 hour |
| Google Quantum AI, Mar 2026 | under 500,000 | minutes |
| IonQ, Sept 8, 2026 | ~20,000 (trapped ion) | ~26 days |
| Largest machines built, 2026 | ~1,100 to 2,500 | cannot run it |
Sources: Quantum Horizon (arXiv, June 2026) for the 2022 and Google figures and current hardware; The Quantum Insider for the IonQ paper. All figures are the authors’ own estimates.
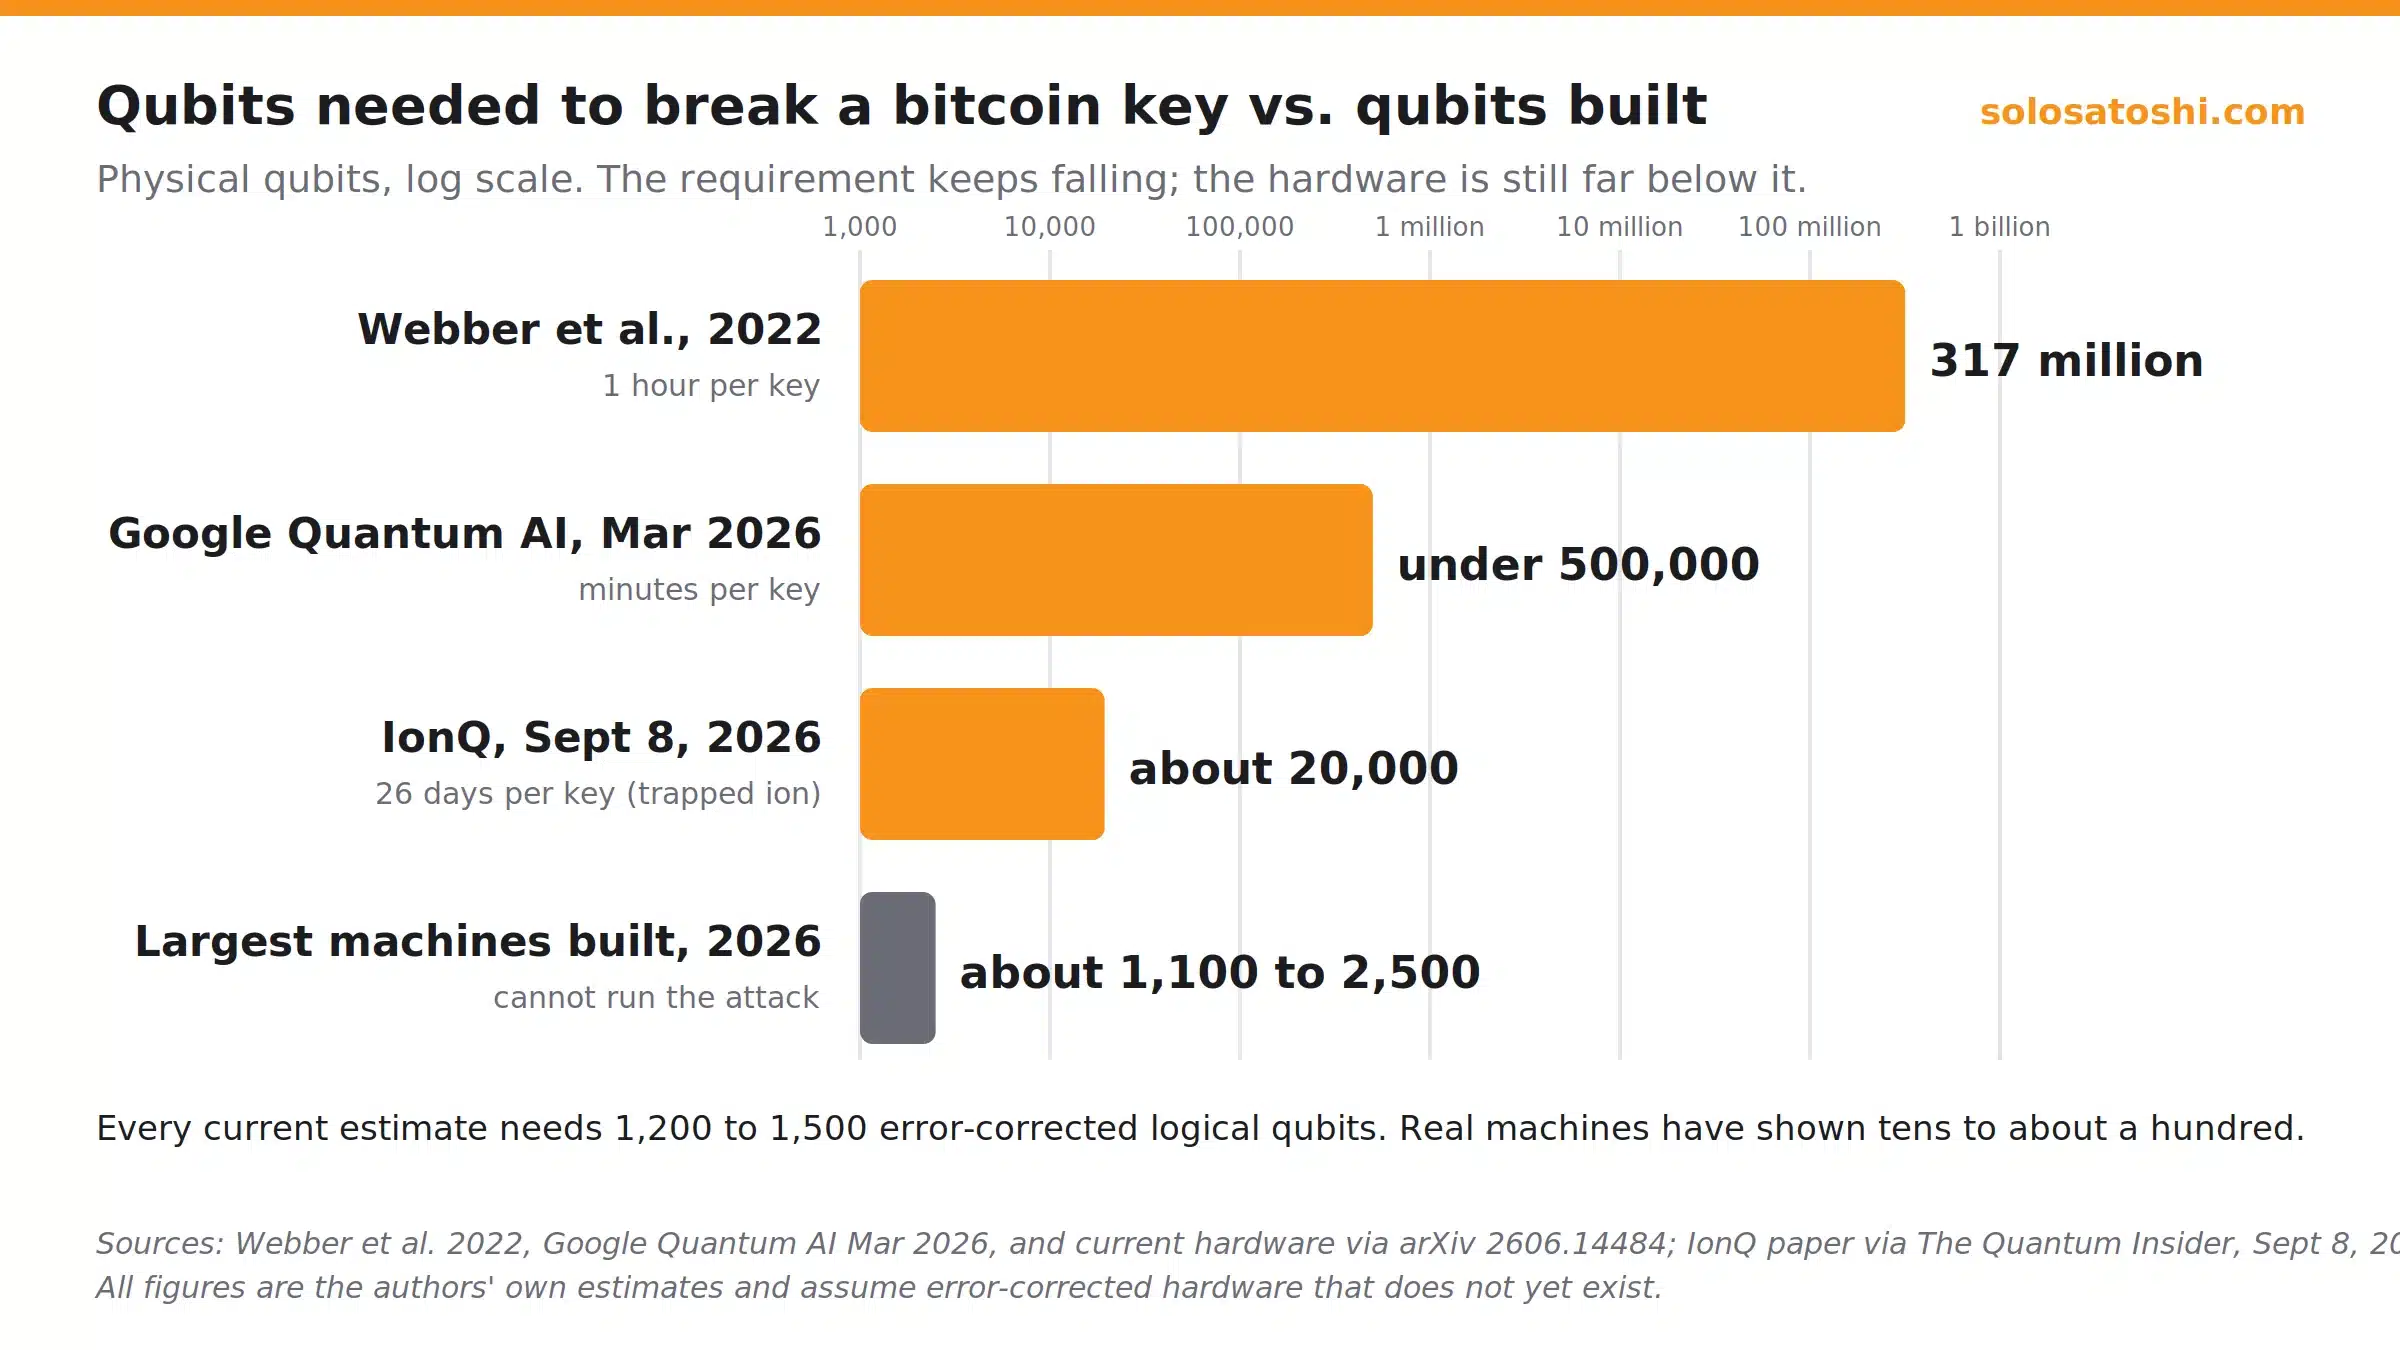
Two things to read from that table. First, the requirement has dropped by four orders of magnitude in four years, and the newest estimate is a paper published the day this article was updated, so the gap is closing faster than most people assumed. Second, the biggest machines that exist hold one or two thousand physical qubits and only tens to about a hundred error-corrected logical qubits, against the 1,200 to 1,500 logical qubits every current estimate requires. A physical qubit is not a working qubit; error correction burns dozens to thousands of them to make one reliable logical qubit, and that overhead is the whole problem. No cryptographically relevant quantum computer exists, and every one of the papers above says so explicitly. Vendor roadmaps talk about 2028 to 2030; independent analysts are more conservative.
Which coins are exposed, and what should you do?
A quantum computer could, in theory, work backward from a public key to the private key that controls it. Your public key is only revealed when you spend from an address (or, for very old pay-to-public-key outputs, from the start). Coins sitting in an address that has never spent are protected by a hash, which is a different problem quantum computers are not expected to solve. Researchers estimate 6 to 7 million BTC currently sit in addresses with exposed public keys, largely from address reuse and Satoshi-era outputs.
The developer community began formal work this year: BIP-360, the first quantum-resistant address proposal, was merged into the BIP repository on February 11, 2026. Merging is documentation, not activation, and the companion migration proposal remains contentious. For now: use a fresh receive address every time (every wallet we sell does this by default), and do not move coins in a panic. There is no action required this year beyond good hygiene, and we will update this section as the hardware and the proposals move.
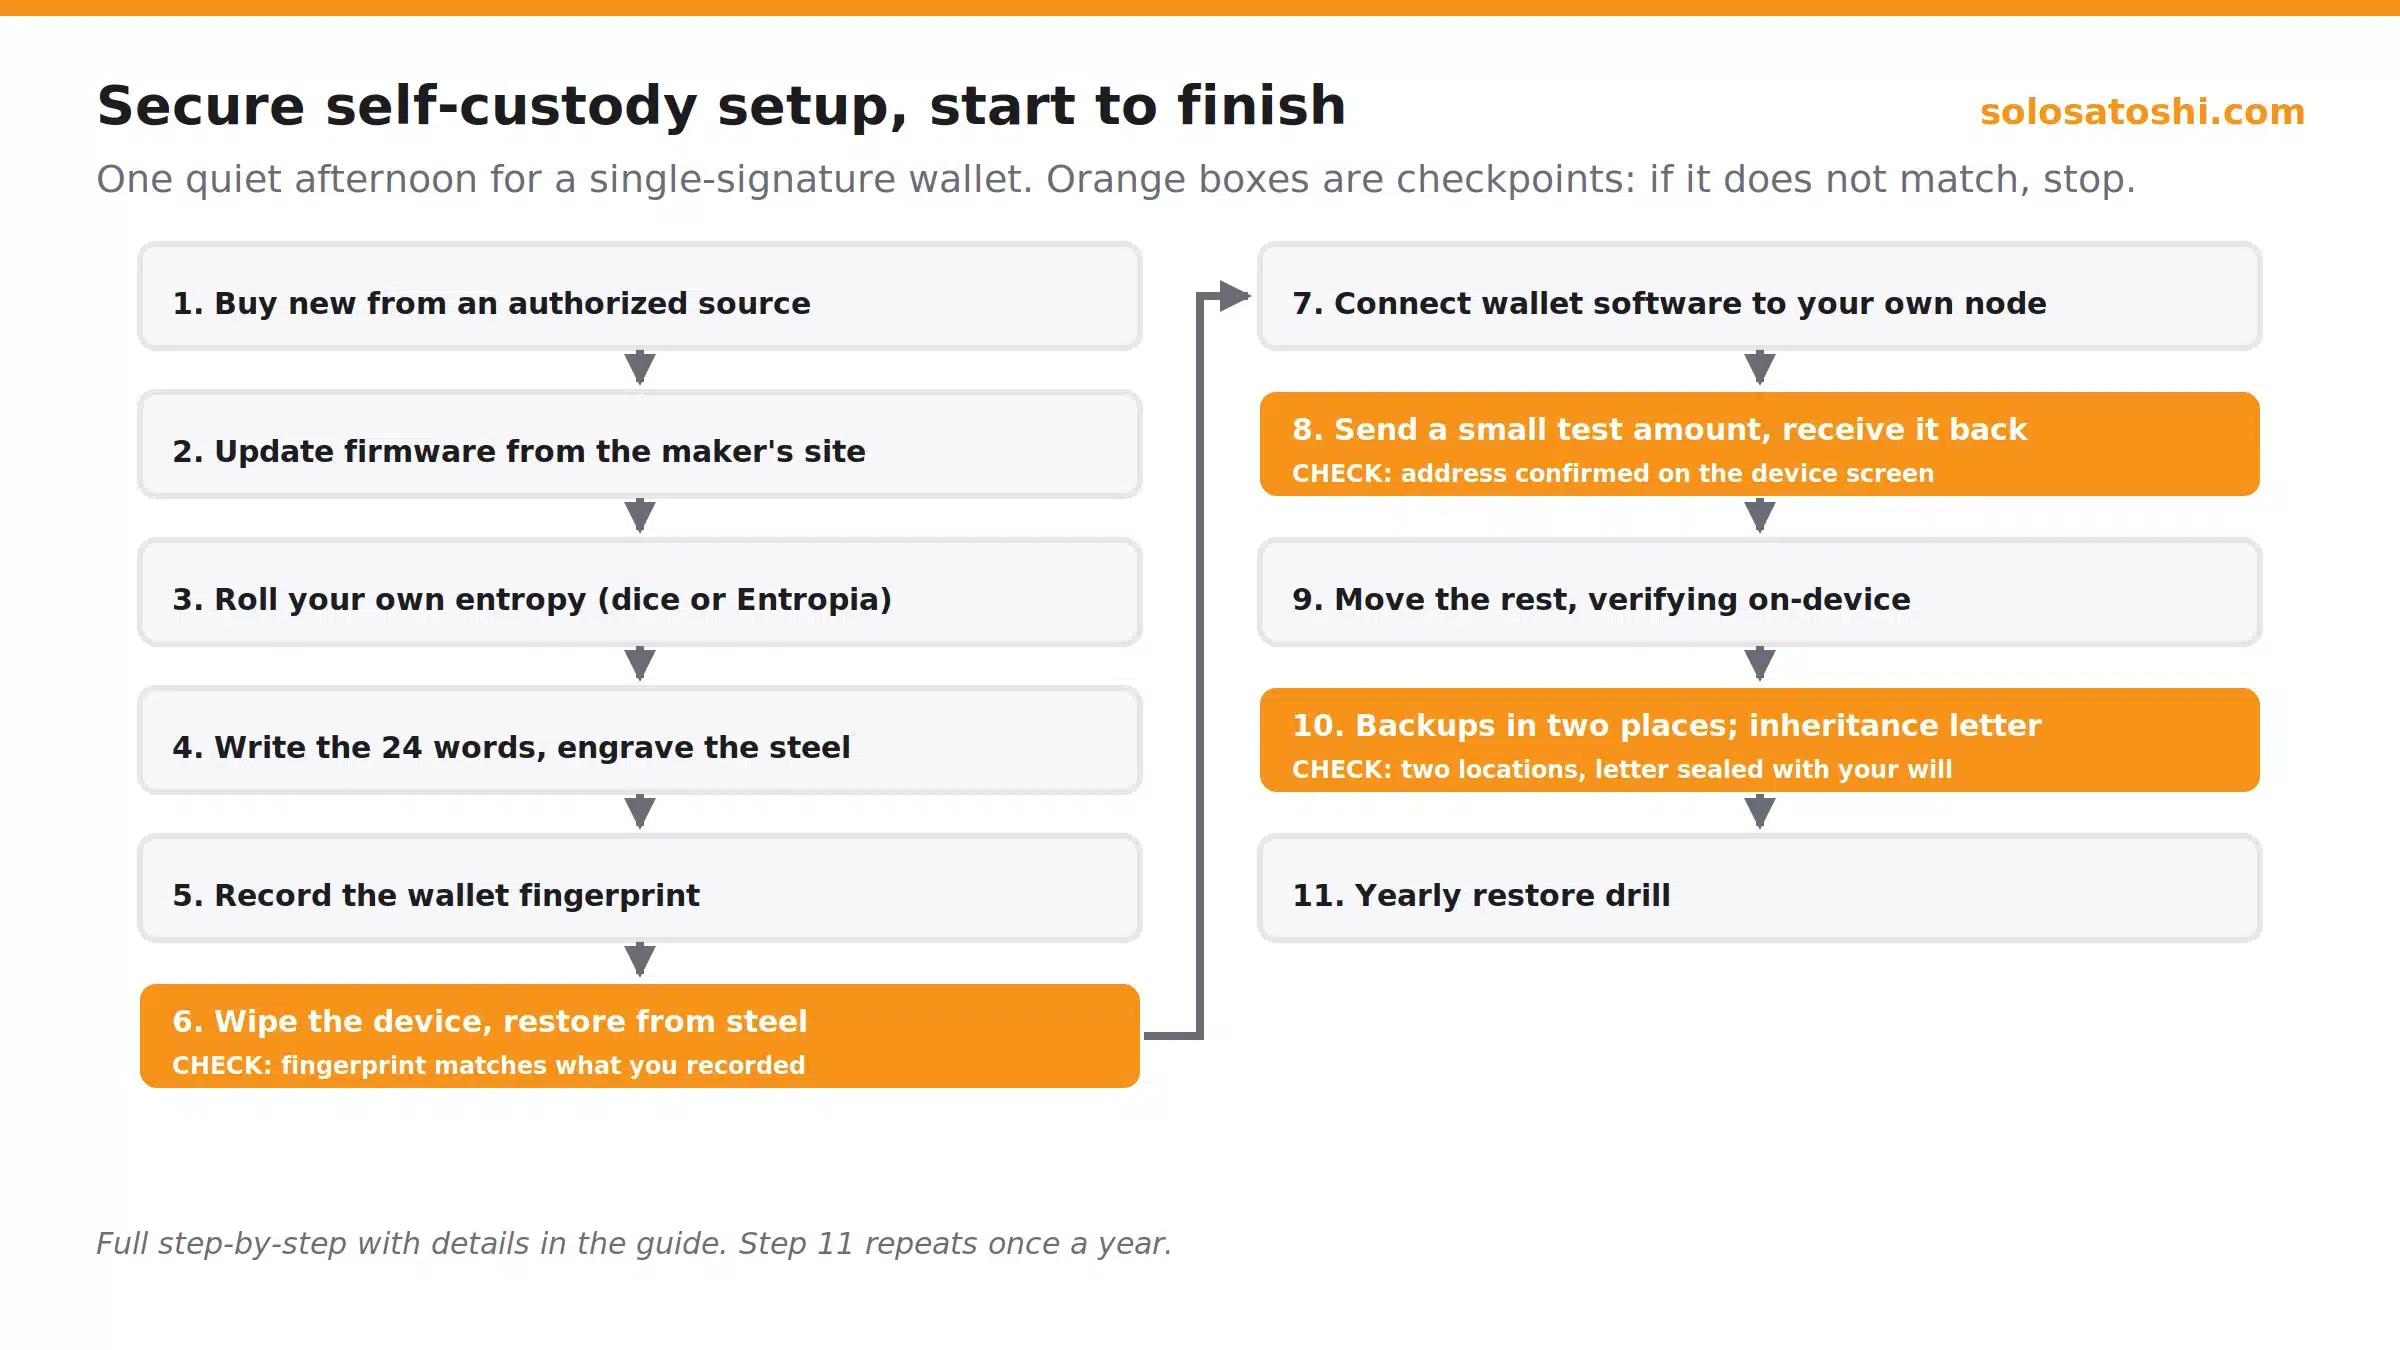
How to set up secure self-custody: step by step
This is the sequence we walk customers through at the counter. Budget one quiet afternoon for a single-signature setup.
- Buy from an authorized source. Inspect the tamper-evident packaging. If anything in the box shows you seed words, stop and contact us.
- Update firmware from the manufacturer’s site. Verify the download signature if the vendor publishes one. Do this before creating a seed.
- Generate the seed with your own entropy. 20 throws of the casino d6 set on the SeedSigner+, 23 throws of the d16/d8 set on the Jade Plus, or 23 Entropia draws with the final word calculated on any of the three signers. Roll in private, off camera.
- Record the 24 words on the recovery card, then engrave the steel plate. Check each word against the BIP39 list as you go. Shred the dice or draw sheet afterward.
- Note the wallet fingerprint. Write it on the steel plate’s label field. It is safe to record and it is how you confirm a future restore is correct.
- Wipe the device and restore from the steel. Confirm the fingerprint matches. Show the first receive address and confirm it matches the one you saw before wiping.
- Connect wallet software to your own node. Point Sparrow, Blockstream App, or Envoy at the Start9’s Electrum server (the part of the node that wallets talk to) so your balance queries stay home.
- Send a small test amount, then receive it back. Verify the address on the device screen both times. Wait for a confirmation.
- Move the rest in one or two transactions. Verify on-device again. Do not copy the address from history.
- Store backups in two locations and write the inheritance letter. Include the device model, the location of each plate, the passphrase location if you use one, and a contact who can help your heirs.
- Schedule a yearly drill. Once a year, restore from steel onto a wiped device and confirm the fingerprint. If a plate has moved, the letter gets updated the same day.
Bottom line
Protecting your bitcoin in 2026 is mostly about defending against people, including yourself. Hold your own keys on a device that shows you what you are signing. Generate the seed with randomness you produced. Put the backup in steel in two places and prove it restores. Say nothing about what you own, and tell your family the plan. Every major loss this year would have been prevented by one of those steps.
The honest trade-off is responsibility. There is no support line that can reverse a mistake, which is exactly why exchanges feel comfortable and exactly why the coins on them are not really yours. The setup takes an afternoon; the habits take a few weeks to feel normal.
Related reading
- Seed Phrase Entropy Explained: Dice, Tablets, and Your Keys
- Bitcoin Wallets 101: An In-Depth Look
- Bitcoin Node: Why Run One? 8 Benefits, Requirements, and Set Up
- What Is a Home Server? The Complete 2026 Guide
What happens to my bitcoin if my hardware wallet company goes out of business?
Can I recover my bitcoin if I lose my hardware wallet?
Is it safe to buy a used or second-hand hardware wallet?
Can someone steal my bitcoin if they know my wallet address?
What happens to my bitcoin when I die?
Is it safe to store my seed phrase in a password manager or cloud drive?
How often should I check on bitcoin in cold storage?
Should I split my bitcoin across multiple wallets?
Do I need to update my hardware wallet's firmware?
Is a mobile wallet safe enough for bitcoin?